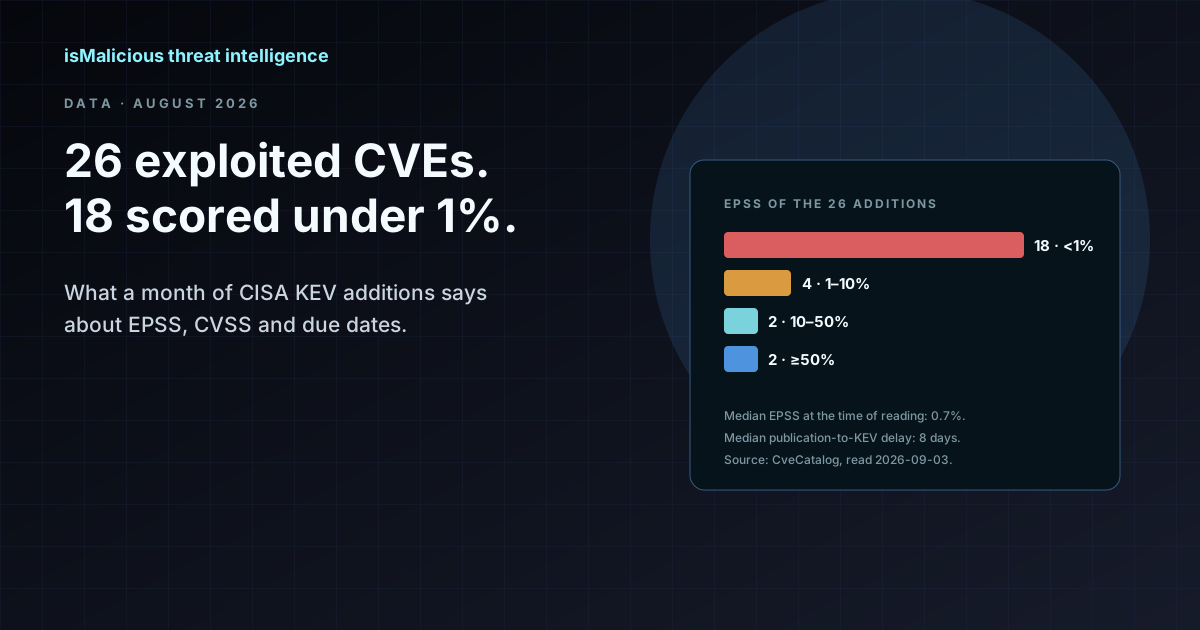
Exploited in August 2026: 26 KEV Additions, 18 With an EPSS Under 1%
A month of CISA KEV additions read against our CVE catalog: 18 of 26 exploited vulnerabilities score under 1% on EPSS today, 4 had no CVSS score when CISA added them, and CISA gave 18 of them a three-day deadline. The numbers, the method, and what they mean for a patch queue.
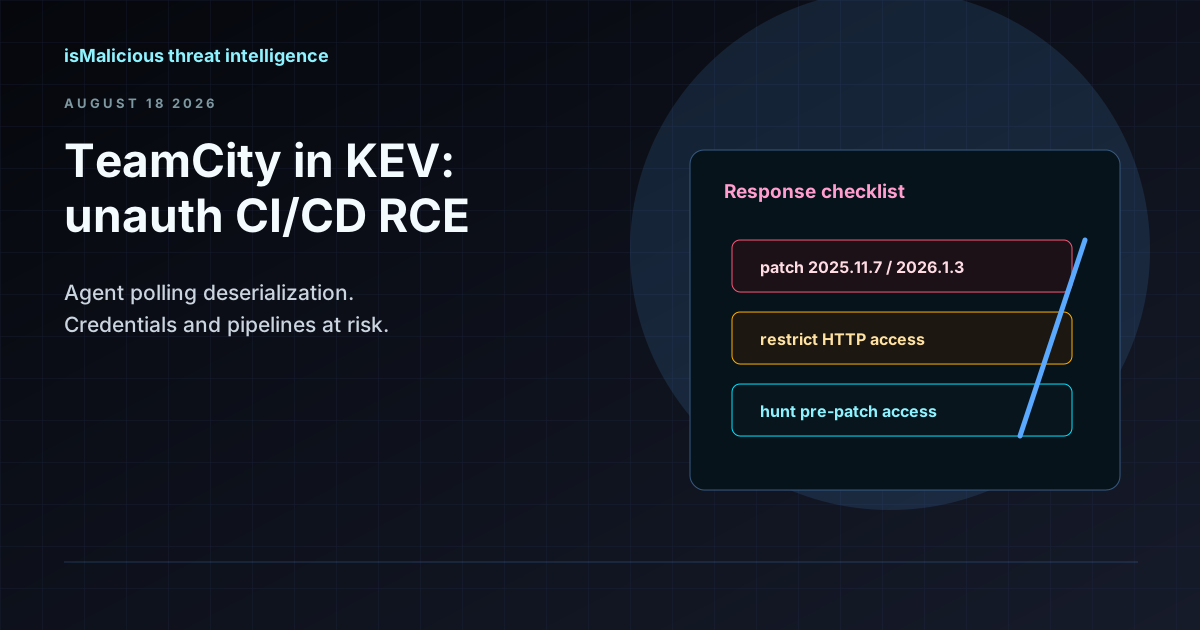
CVE-2026-63077 Puts Unauthenticated RCE on Every TeamCity On-Premises Server
A deserialization flaw in the agent polling protocol gives attackers TeamCity server privileges without credentials. JetBrains patched in 2025.11.7 and 2026.1.3 — CISA KEV and a 3-day federal deadline mean hunt now, not after the next release train.
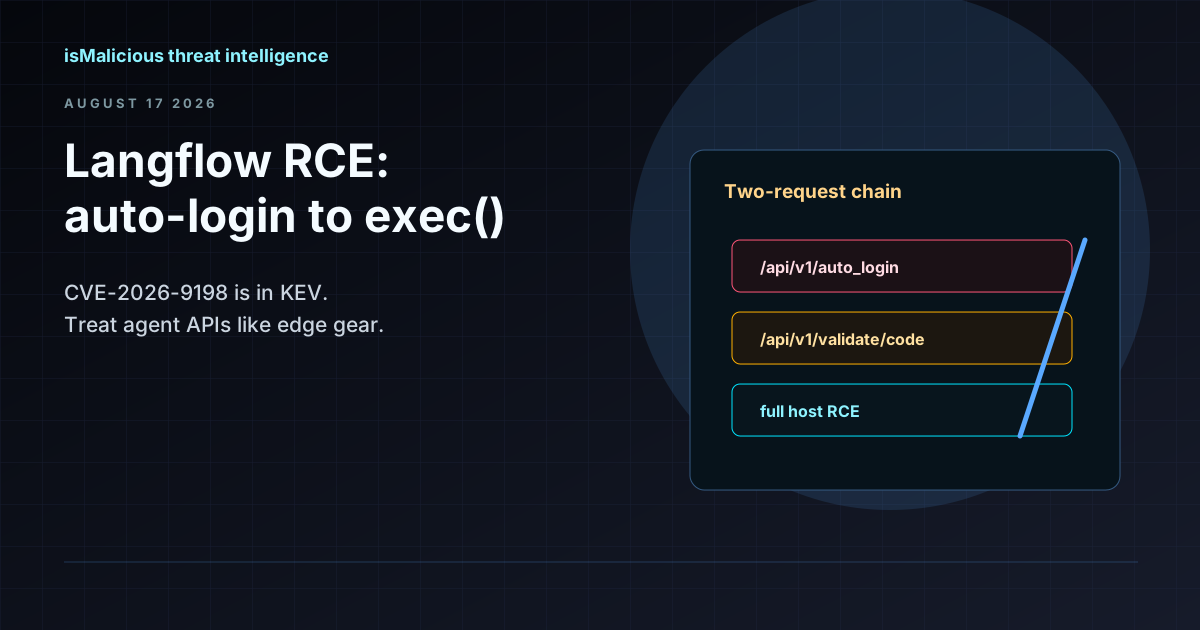
CVE-2026-9198 Gives Unauthenticated RCE in IBM Langflow OSS Agent Control Planes
A SUPERUSER token minted through /api/v1/auto_login chains with Python exec() in /api/v1/validate/code. Langflow 1.10.1 fixes the flaw — but internet-exposed instances need hunting now, not after the next sprint.
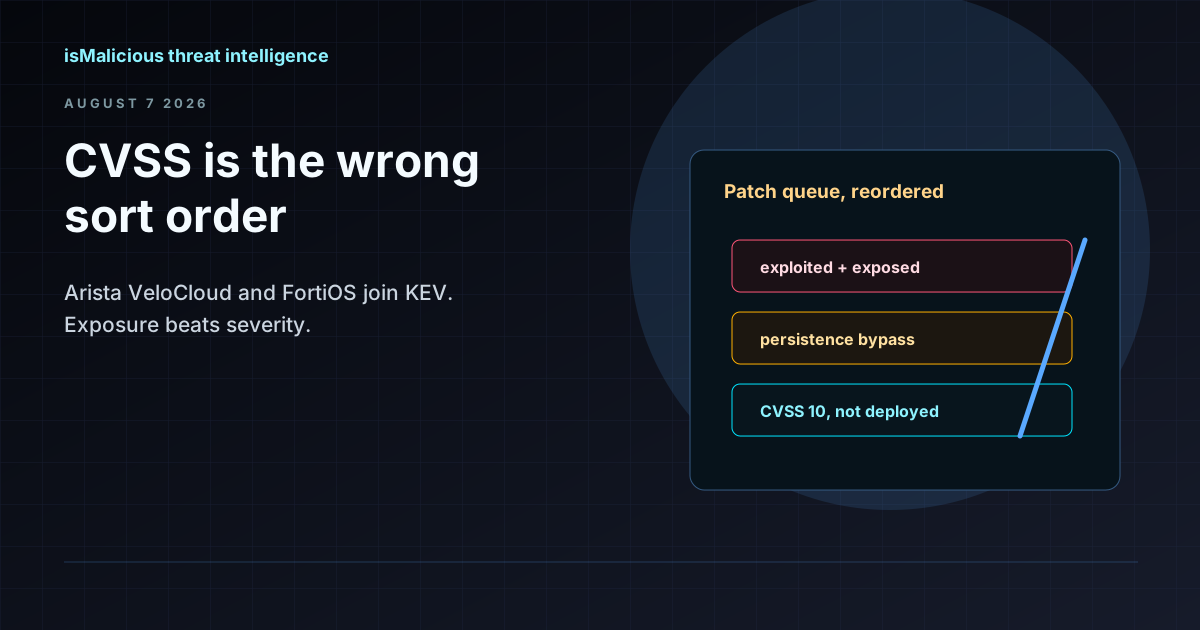
CISA KEV Adds Arista VeloCloud and FortiOS Flaws: Why CVSS Is the Wrong Sort Order
On 27 July 2026 CISA added a CVSS 10.0 command injection in Arista VeloCloud Orchestrator and a medium-severity FortiOS patch bypass to KEV. The pairing shows why exposure and persistence beat severity when ordering a patch queue.
BlueHammer Defender Exploitation: July 2026 Patch SLA For Windows Fleets
BlueHammer coverage shows why endpoint patching, CISA KEV context, CVE Watch, and IOC enrichment have to work together when local privilege escalation becomes ransomware tradecraft.
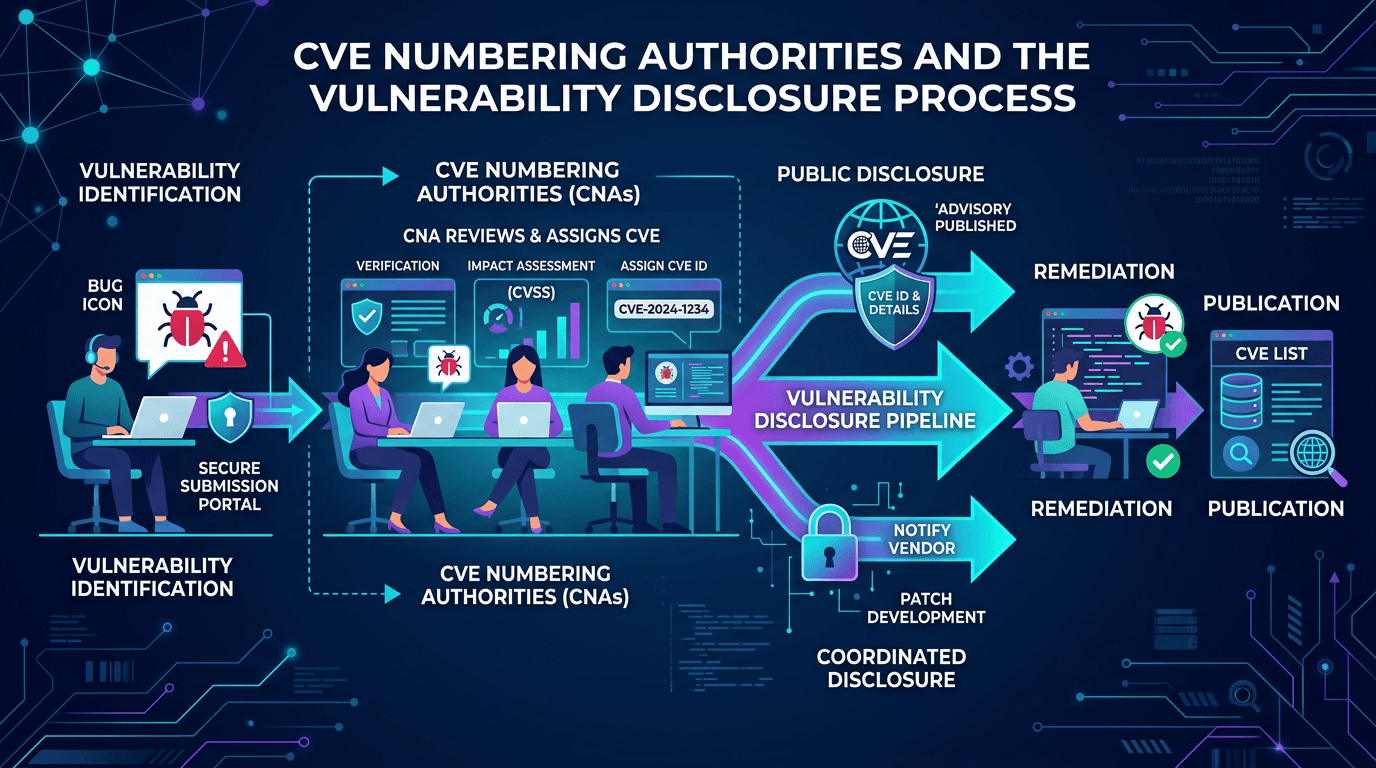
CVE Numbering Authorities and the Vulnerability Disclosure Process: A 2026 Practitioner Guide
Understand how CVEs are born—from initial vulnerability discovery through CNA assignment, coordinated disclosure, and publication—plus how this pipeline shapes defender priorities and SEO-visible vulnerability data.

EPSS vs CVSS vs KEV: How to Prioritize CVEs When Everything Looks Critical
Cut through scoring confusion: compare CVSS severity, EPSS exploit probability, and CISA KEV active exploitation—and learn a practical model for patch and compensating-control decisions.

EPSS Explained: Using the Exploit Prediction Scoring System to Prioritize Patches in 2026
A practical guide to the Exploit Prediction Scoring System (EPSS)—how it works, how it complements CVSS and KEV, and how security teams can use EPSS probabilities to prioritize vulnerability management at scale.
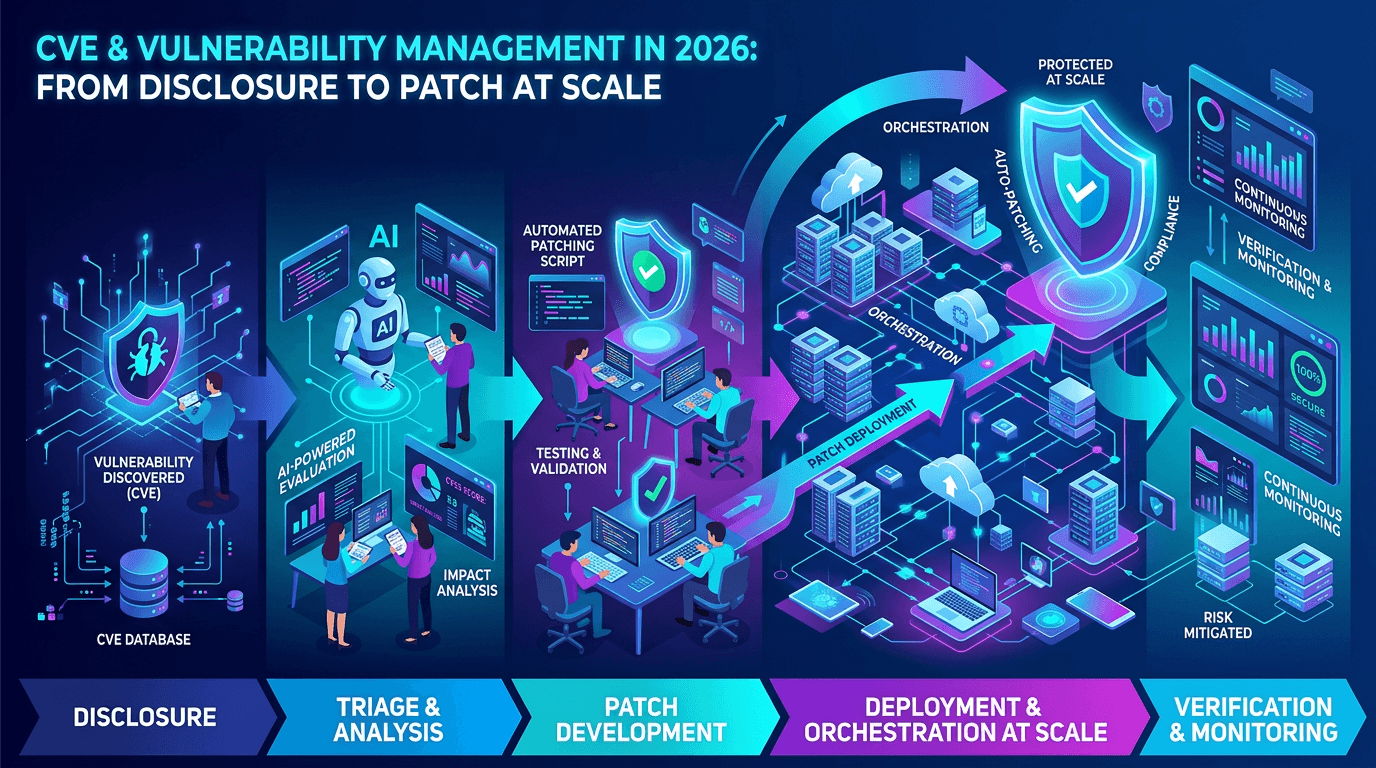
CVE & Vulnerability Management in 2026: From Disclosure to Patch at Scale
A practical guide to the CVE ecosystem, CVSS scoring, exploitability signals, and how security teams prioritize vulnerabilities without drowning in scanner noise.

CVSS 4.0 Explained: A Complete Guide to Vulnerability Severity Scoring in 2026
Master the Common Vulnerability Scoring System v4.0 with a practical breakdown of base, threat, environmental, and supplemental metrics—and learn how to translate CVSS into real-world risk decisions.