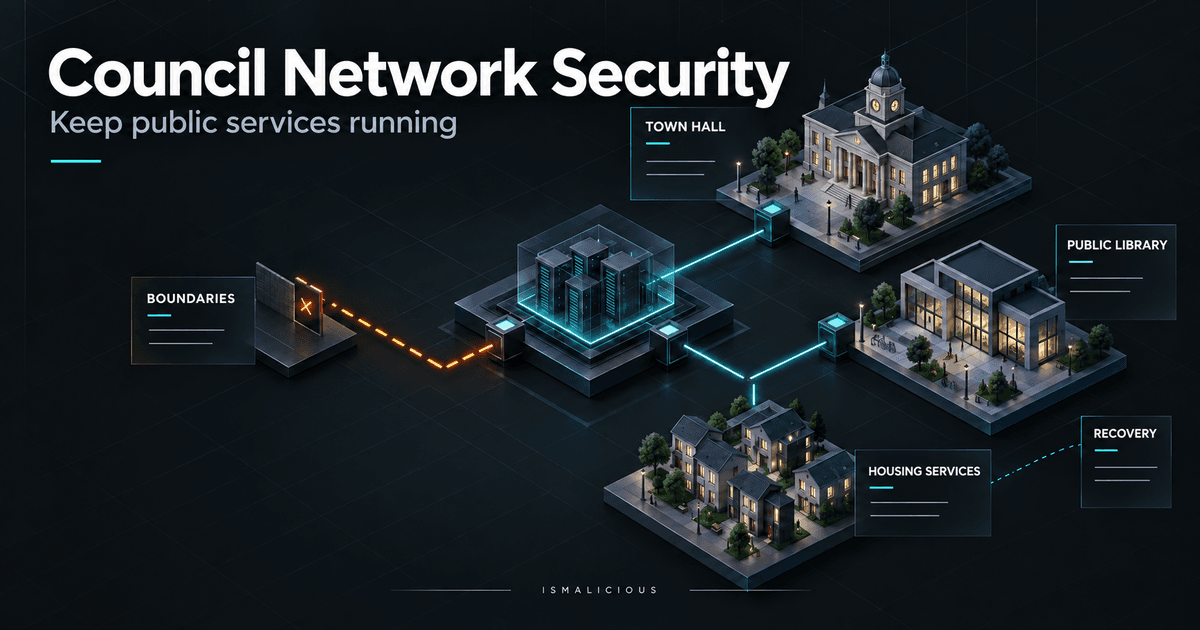
Local Government Network Security: A 90-Day Council Plan
Build a council network security plan around public services, clear ownership, tested segmentation and useful logs, with practical actions across 90 days.
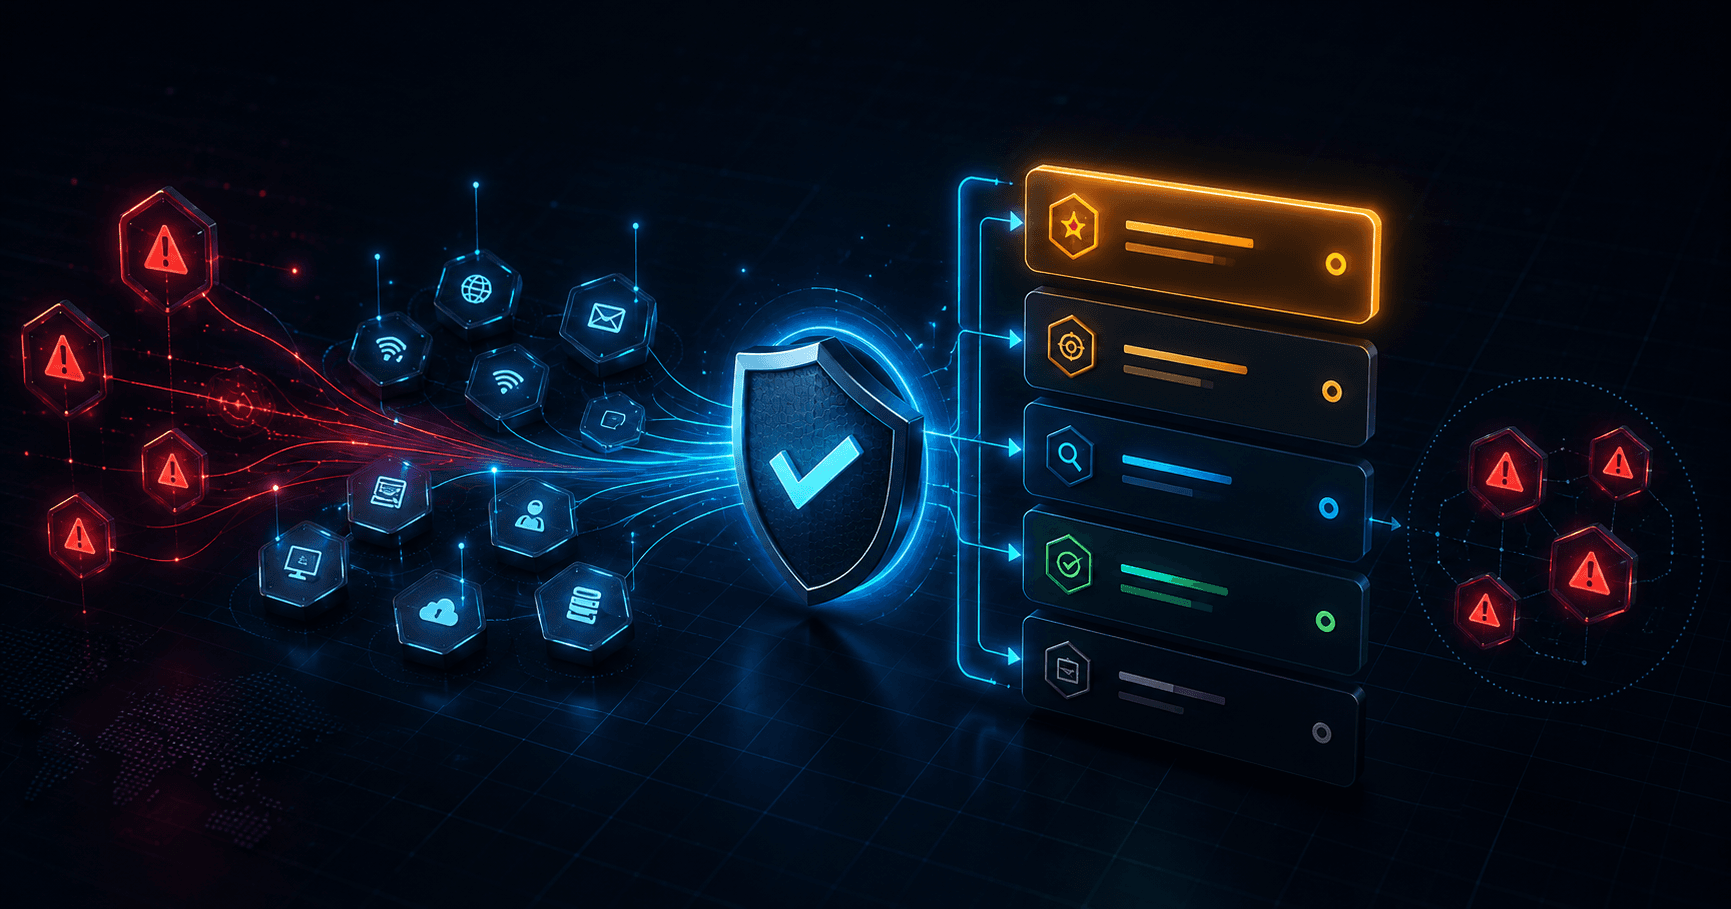
Threat Alerts and Action Center: Build a Response Workflow
Move from monitored indicators and incoming alerts to a ranked queue, analyst validation, and owned response work with isMalicious Alerts and Action Center.

Blocklists for Operational Threat Prevention: Test and Roll Back
Use /app/blocklists to select, test, deploy, measure, and safely reverse IP or domain prevention controls.
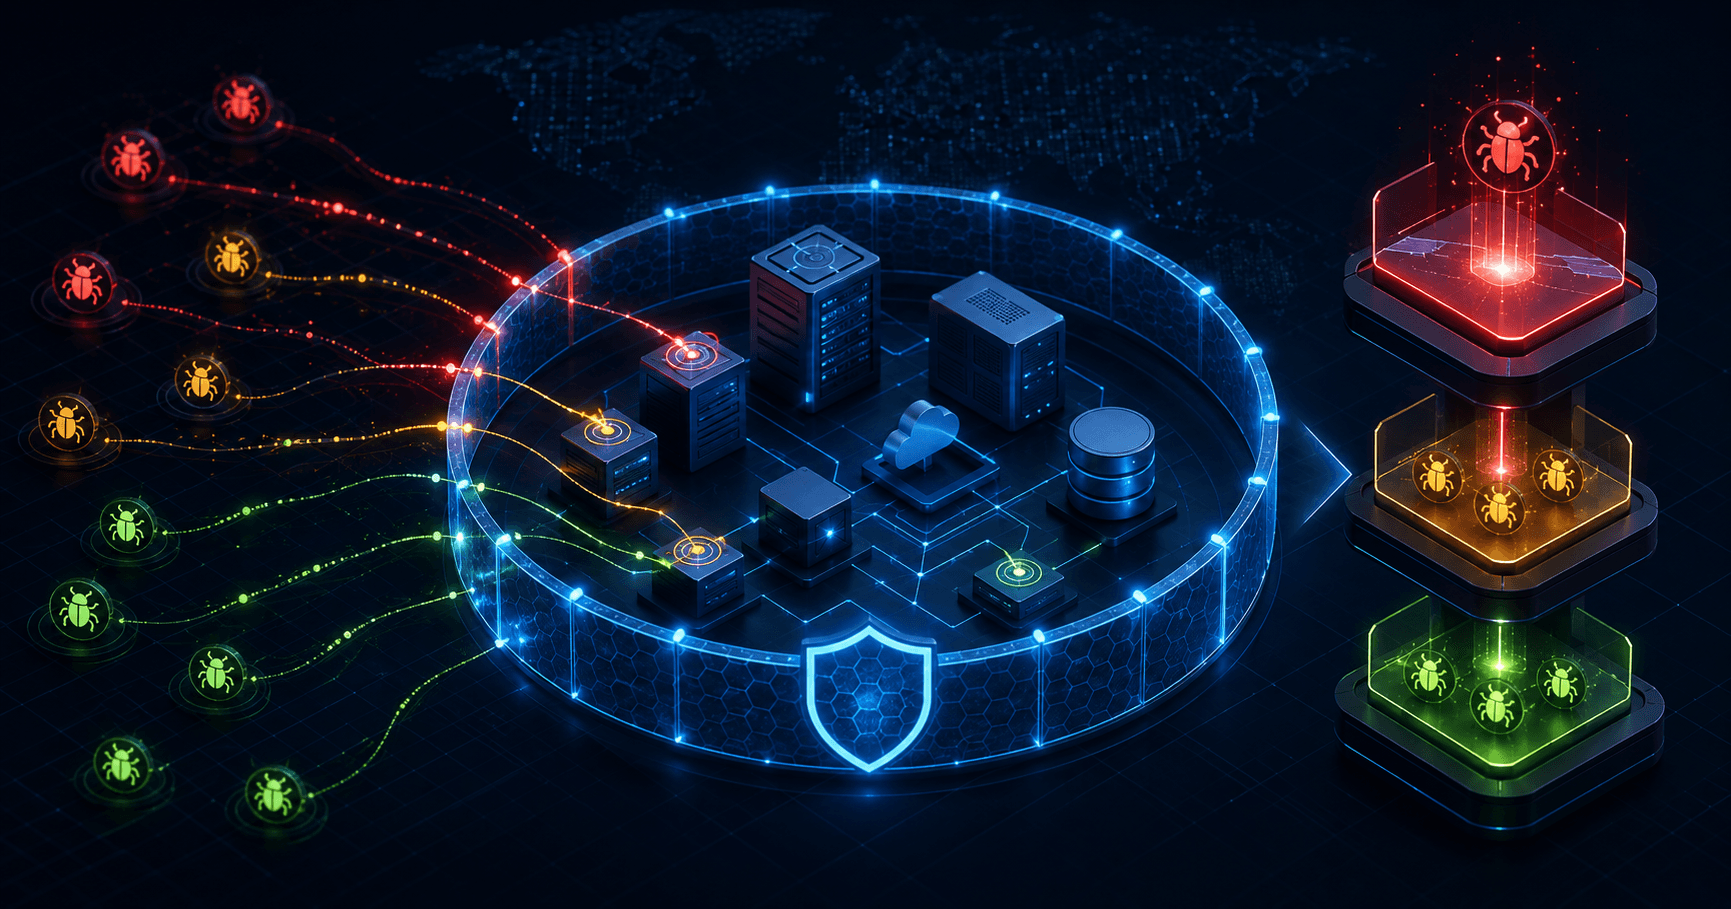
CVE Watch Perimeters: Prioritize Findings by Real Exposure
Map products to CVE Watch perimeters, then combine active exploitation, CISA KEV, EPSS, CVSS, product context, and remediation status to focus vulnerability work.
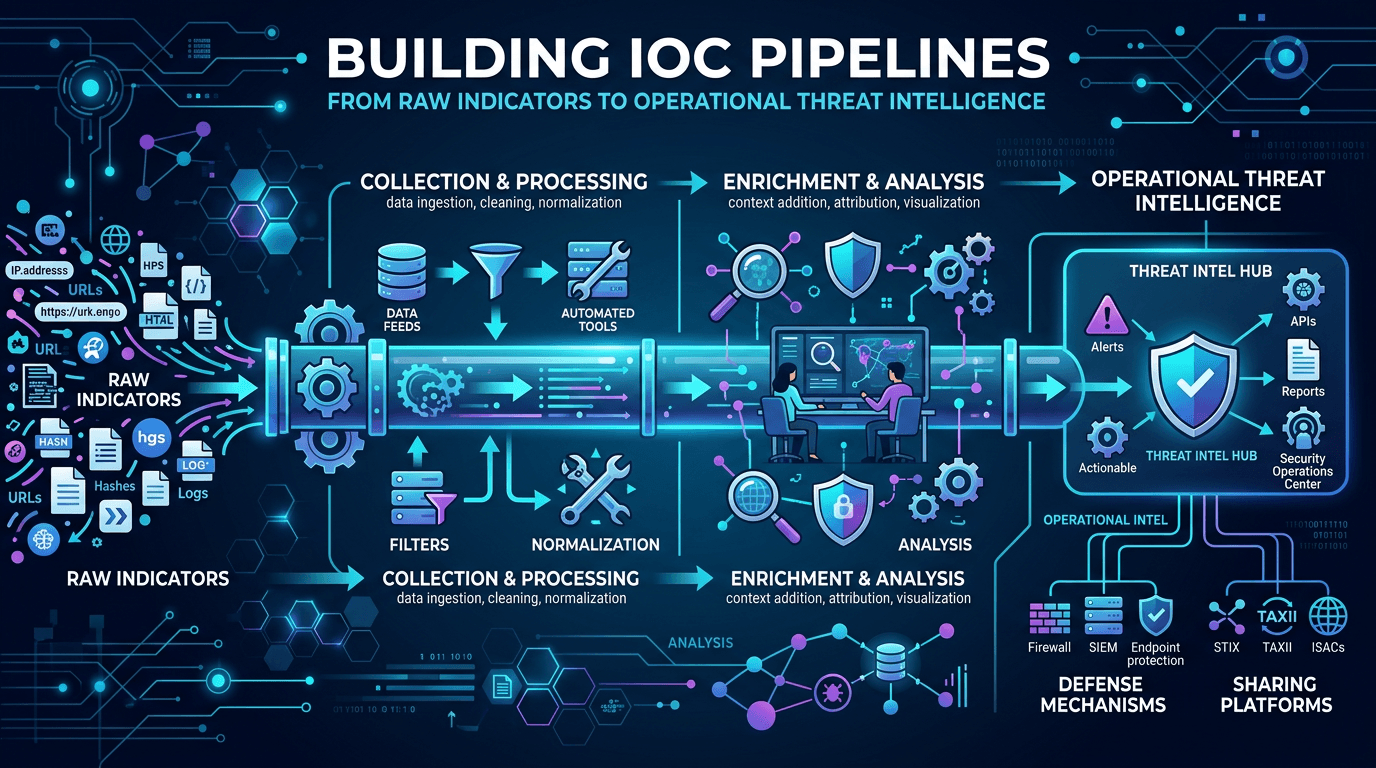
Building IOC Pipelines: From Raw Indicators to Operational Threat Intelligence in 2026
A practical engineering guide to building indicator of compromise (IOC) pipelines—ingestion, normalization, deduplication, enrichment, scoring, distribution, and feedback—to turn raw threat feeds into operational defense.
OSINT for SOC Analysts: Turning Open Source Intelligence Into Threat intelligence analysts can use
A complete guide to open source intelligence (OSINT) for security operations—tools, techniques, workflows, and legal considerations for collecting, analyzing, and operationalizing open threat data in a modern SOC.
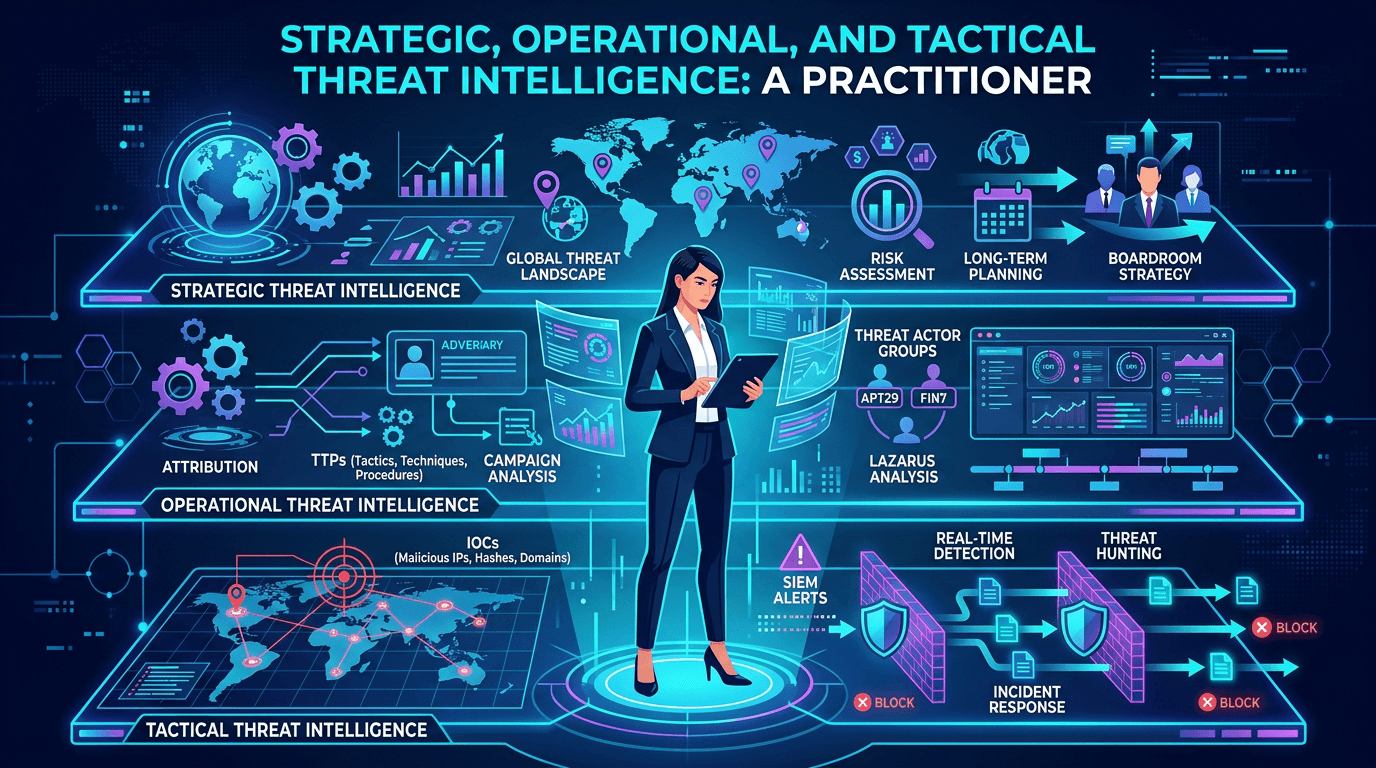
Strategic, Operational, and Tactical Threat Intelligence: A Practitioner's Framework for 2026
A complete guide to the three levels of threat intelligence—strategic, operational, and tactical—with practical examples of consumers, outputs, feeds, and how to connect them into a coherent CTI program.
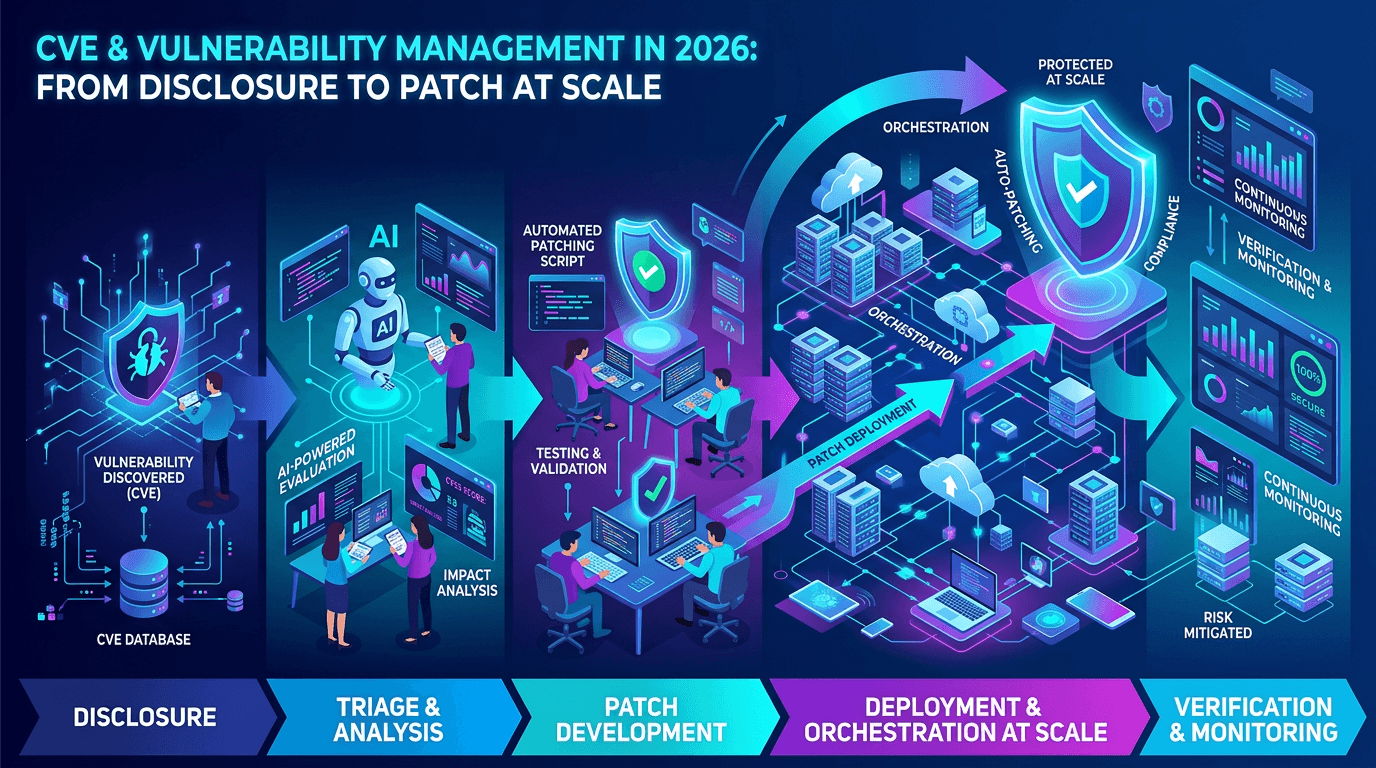
CVE & Vulnerability Management in 2026: From Disclosure to Patch at Scale
A practical guide to the CVE ecosystem, CVSS scoring, exploitability signals, and how security teams prioritize vulnerabilities without drowning in scanner noise.