RDAP: Read Domain Data During an Investigation
Use RDAP events, statuses, and contacts to document a suspicious domain without misattributing an identity or claiming an unproven compromise.
Smart Lookup: Check Any Threat Indicator from One Search
Paste an IP, domain, URL, email, phone number, wallet, file hash, or a complete suspicious message. Smart Lookup routes each indicator to the right threat report.
isMalicious API: Make Your First Reliable IOC Lookup
Call the current isMalicious IOC endpoint safely, handle failures, log useful evidence, and move from a terminal test to production.
Threat Report History: Recheck, Monitor, and Reuse Evidence
Use isMalicious report history to find earlier lookups, run fresh checks, add indicators to monitoring, create cases, and export a reusable lookup index.
Threat Intelligence Sources: Evaluate Evidence Before You Act
Use isMalicious Sources and Threat Patterns to examine freshness, contribution, agreement, coverage, and corpus-wide patterns before turning a detection into action.

isMalicious vs Spamhaus: DNSBL Blocklists and Threat Enrichment Serve Different Layers
Spamhaus DROP and SBL are the standard for mail and network DNSBL blocking. isMalicious adds REST enrichment, URL scoring, CVE context, and STIX feeds. Most mature stacks use both at different layers.
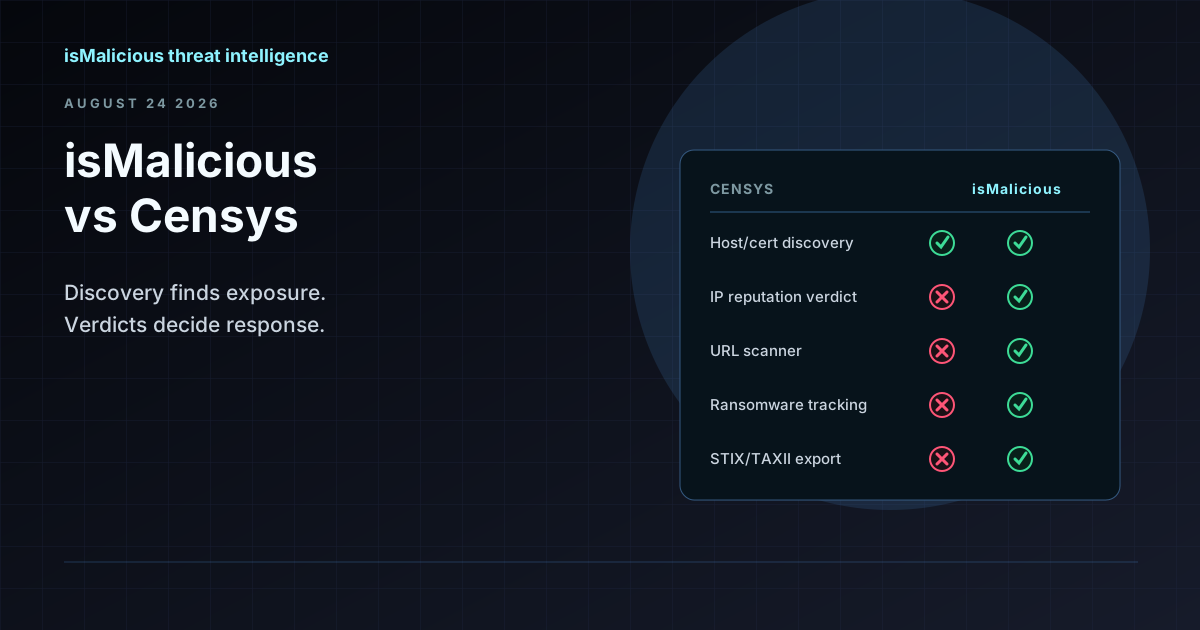
isMalicious vs Censys: Internet Discovery and Reputation Verdicts Are Different Jobs
Censys maps what exists on the internet — hosts, certificates, open ports. isMalicious assesses what is malicious. Most teams comparing the two need the second question answered, not the first.
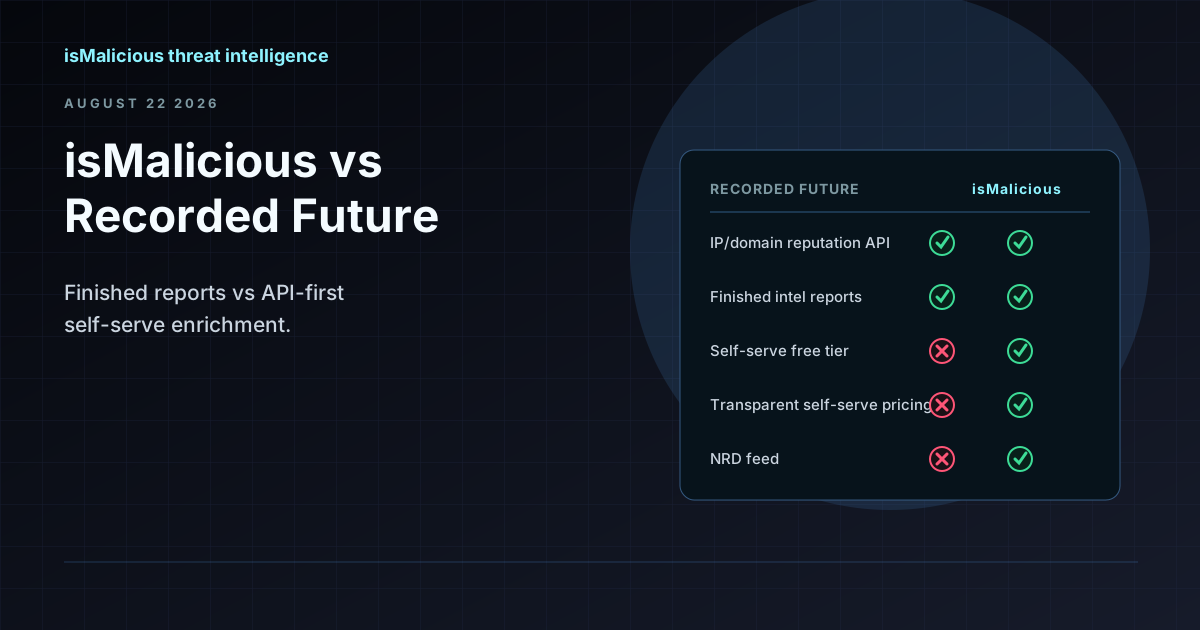
isMalicious vs Recorded Future: When a Threat Data API Makes More Sense Than an Enterprise Intel Program
Recorded Future delivers finished intelligence and analyst support at enterprise scale. isMalicious delivers self-serve enrichment and feeds without a sales cycle. The right choice depends on whether you need strategic reports or automated verdicts.
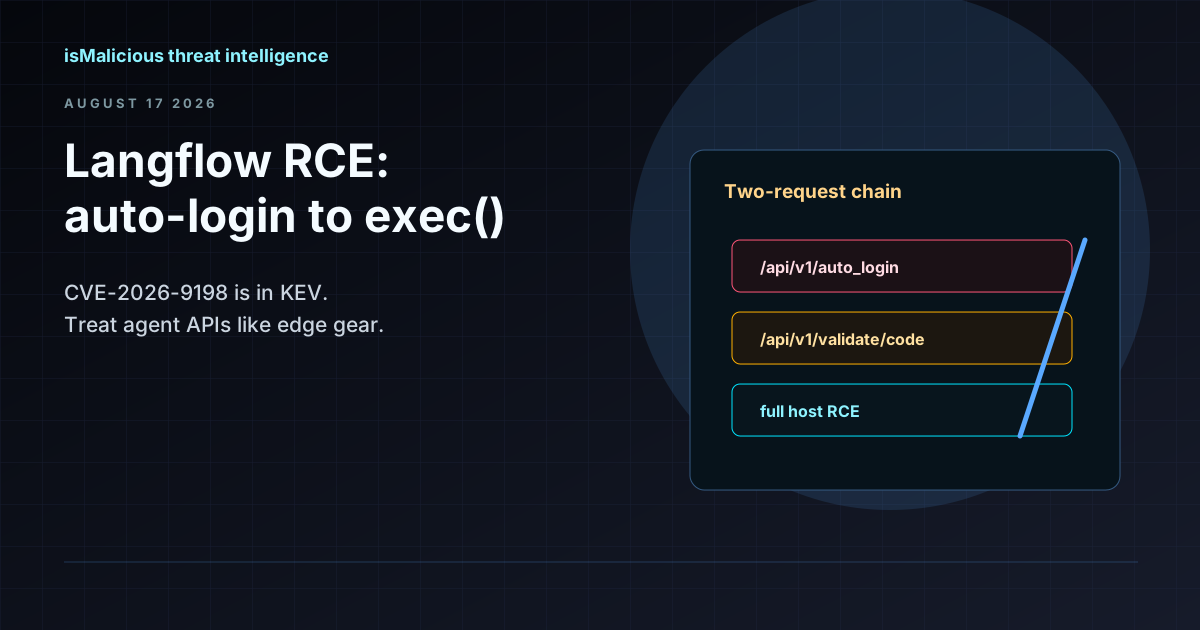
CVE-2026-9198 Gives Unauthenticated RCE in IBM Langflow OSS Agent Control Planes
A SUPERUSER token minted through /api/v1/auto_login chains with Python exec() in /api/v1/validate/code. Langflow 1.10.1 fixes the flaw — but internet-exposed instances need hunting now, not after the next sprint.
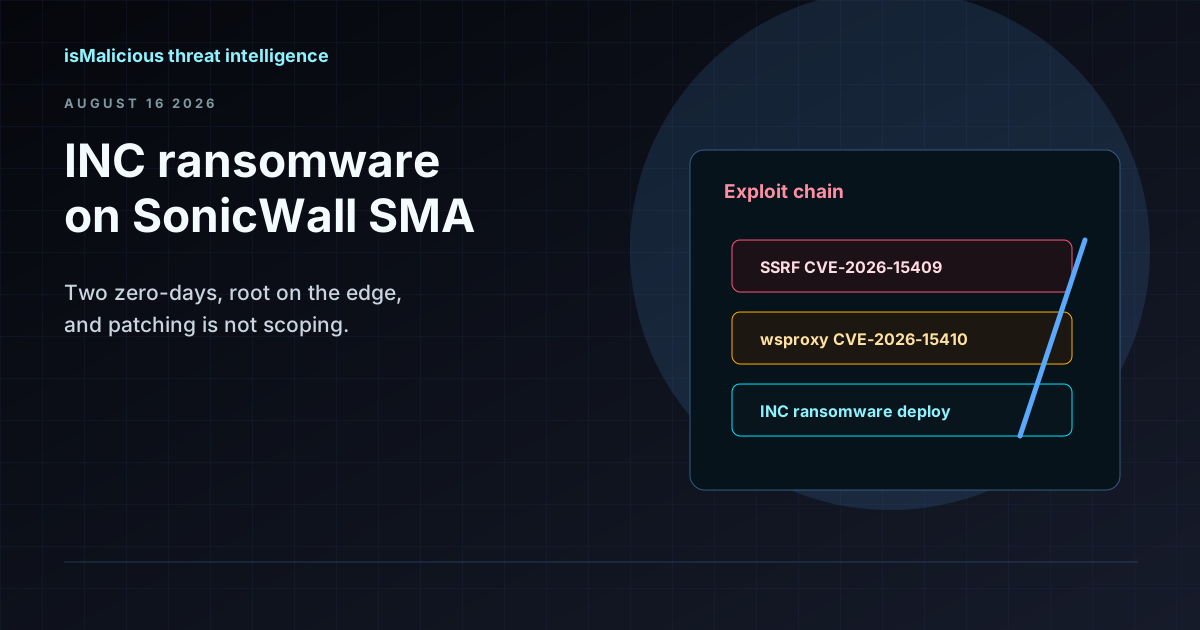
INC Ransomware Chains Two SonicWall SMA Zero-Days (CVE-2026-15409, CVE-2026-15410)
INC affiliates are weaponizing an SSRF and a post-authentication code injection in SonicWall SMA 1000 to reach internal networks. Exploitation started weeks before the July 14 patch — here is how to hunt and triage.
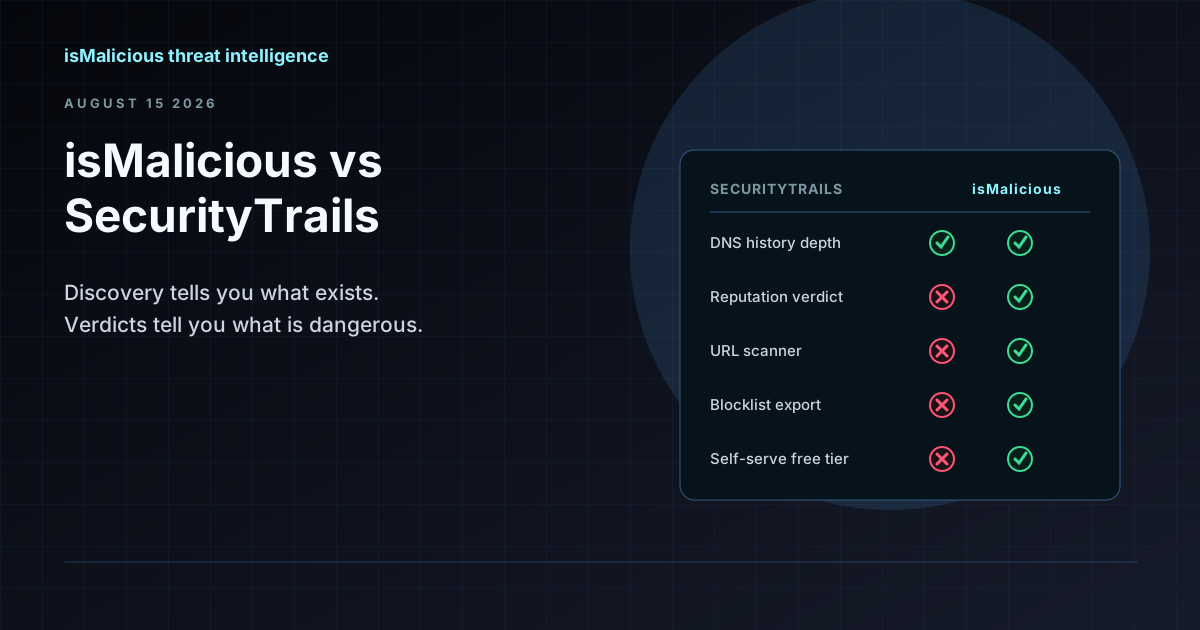
isMalicious vs SecurityTrails: Discovery Data and Reputation Verdicts Are Not the Same Product
SecurityTrails tells you what exists — every subdomain, every historical DNS record. isMalicious tells you what is dangerous. Most teams searching for a SecurityTrails alternative want the second half.
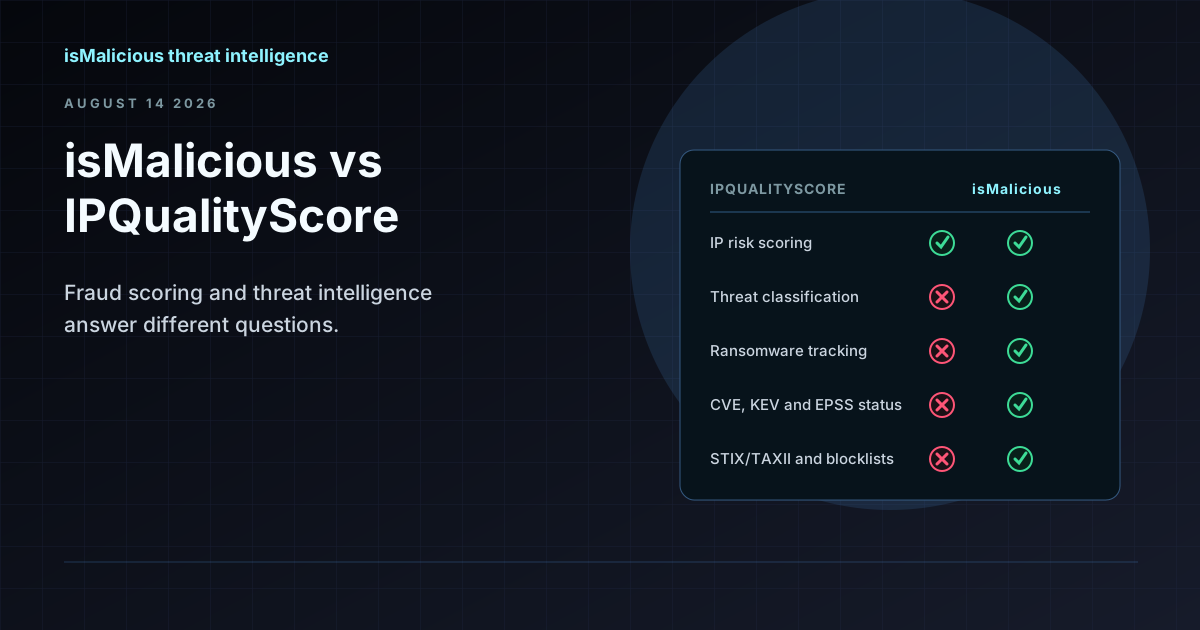
isMalicious vs IPQualityScore: Fraud Scoring and Threat Intelligence Are Different Jobs
IPQS scores whether a signup is fraudulent. isMalicious scores whether infrastructure is malicious. The two get compared constantly because both return a number about an IP address — and they answer different questions.
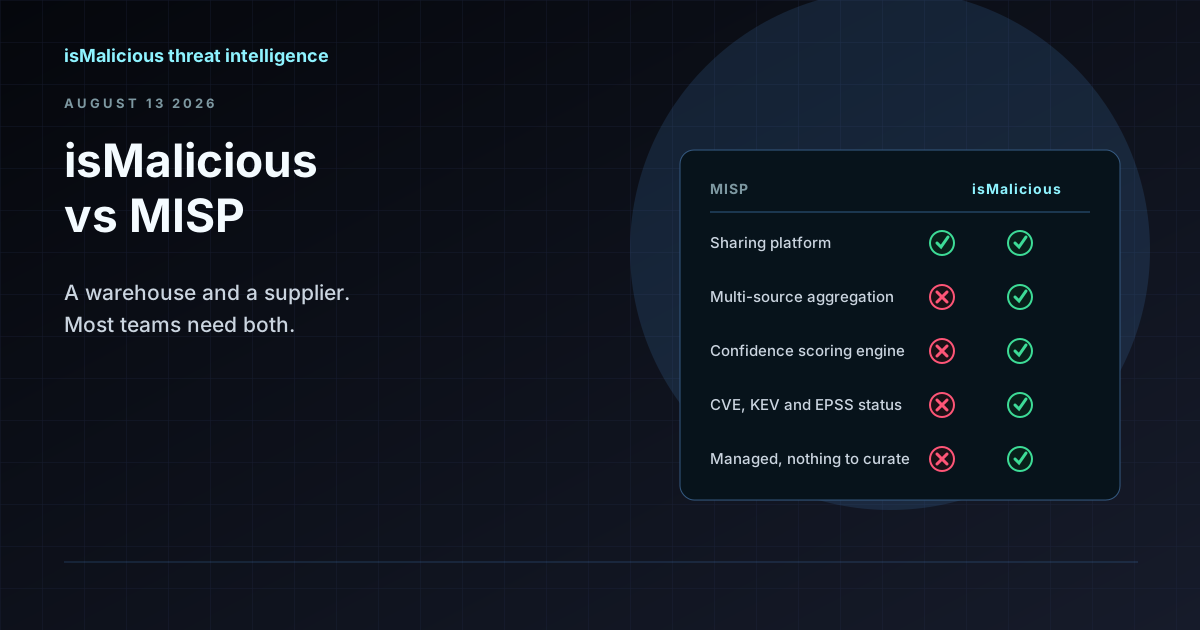
isMalicious vs MISP: Why This Is the Wrong Comparison (and What to Compare Instead)
MISP is where you store and share indicators. isMalicious is where indicators come from. Teams searching for a MISP alternative are usually looking for a feed, not a replacement platform.
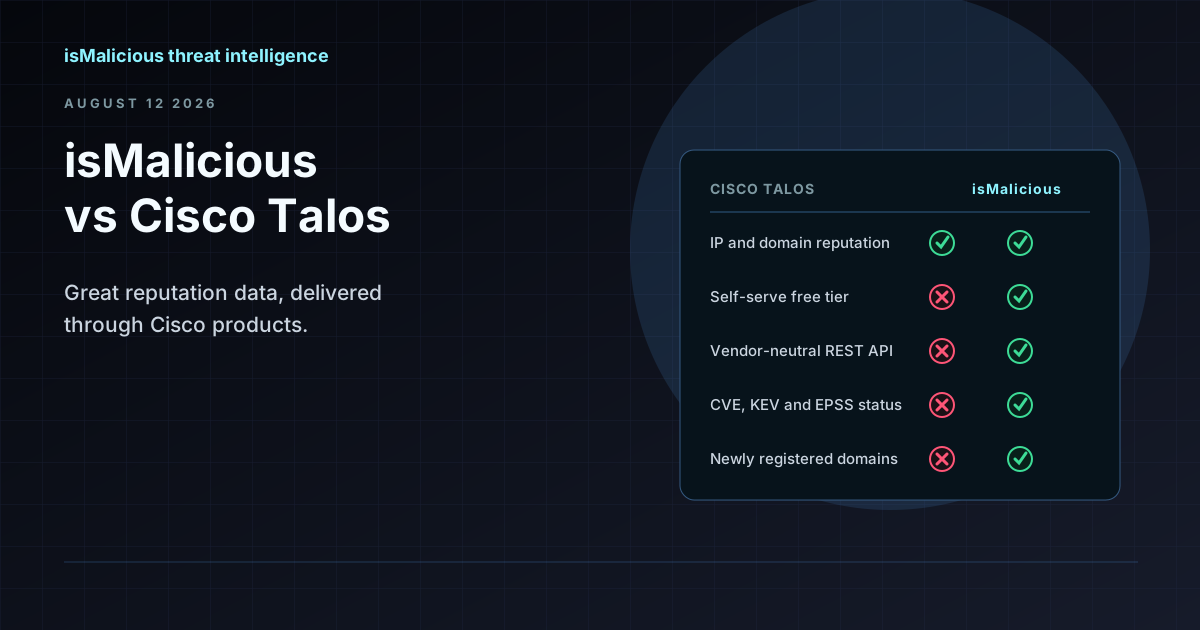
isMalicious vs Cisco Talos: Reputation Lookups Outside the Cisco Stack
Talos reputation is excellent and it lives inside Cisco products. If your stack is not Cisco, or you need an API rather than a web form, that is where the comparison starts.
Bulk IP and Domain Lookups: Designing Indicator Enrichment That Survives Real Volume
One incident produces hundreds of indicators, and per-indicator lookups are where triage stalls. Here is how to build a batch enrichment pipeline that respects quotas, deduplicates properly, and fails gracefully.
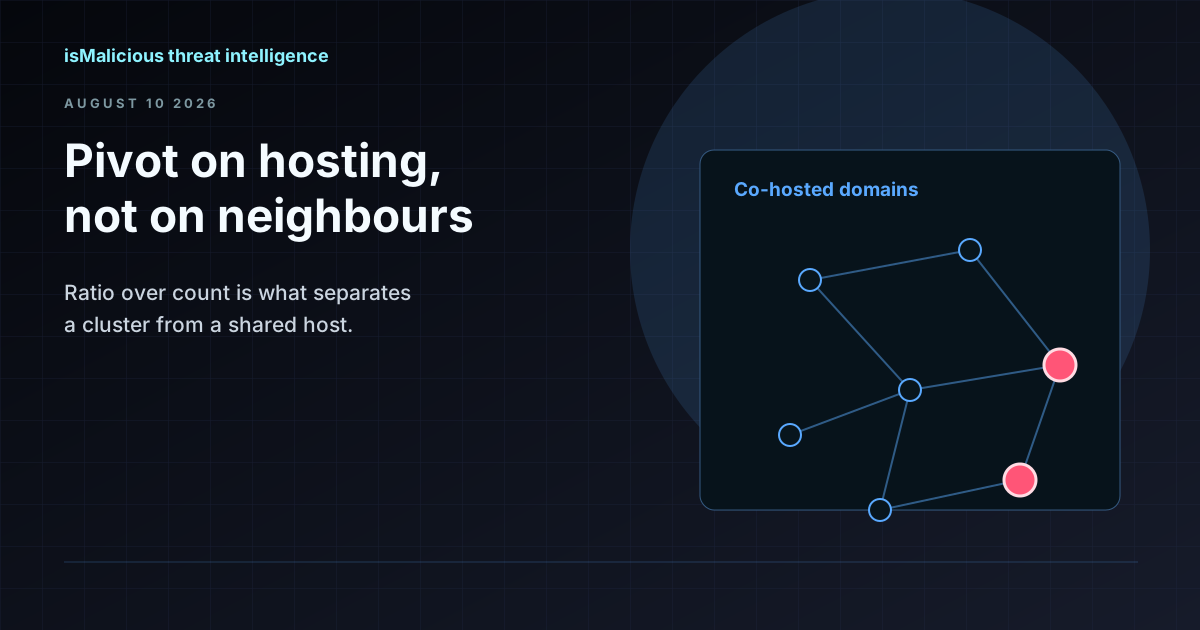
Reverse IP Lookup: Pivoting on Infrastructure Without Drowning in Shared Hosting
A reverse IP lookup turns one indicator into a cluster — or into a thousand innocent neighbours. Here is how to tell the difference, and how to pivot on hosting infrastructure without generating false positives.
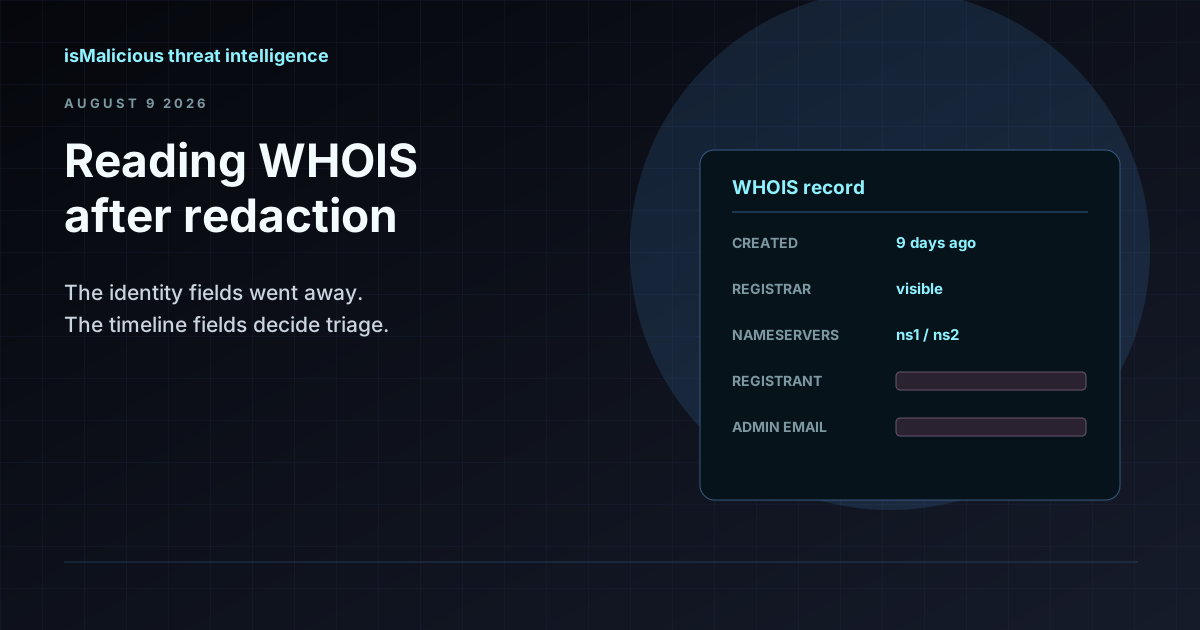
WHOIS Lookup for Security Investigations: Reading a Record After Redaction
Privacy services stripped the registrant name out of most WHOIS records, but the fields that matter for triage survived. Here is what a WHOIS record still tells an analyst, and how to read it.
The Kratos Phishing Kit Takedown: 200 Servers Gone, 1,800 Copies Still Out There
German and US law enforcement dismantled Kratos, the AiTM phishing service behind roughly 15,000 Microsoft 365 campaigns a month. The infrastructure is offline, but the kit is not. Here is what to hunt for now.
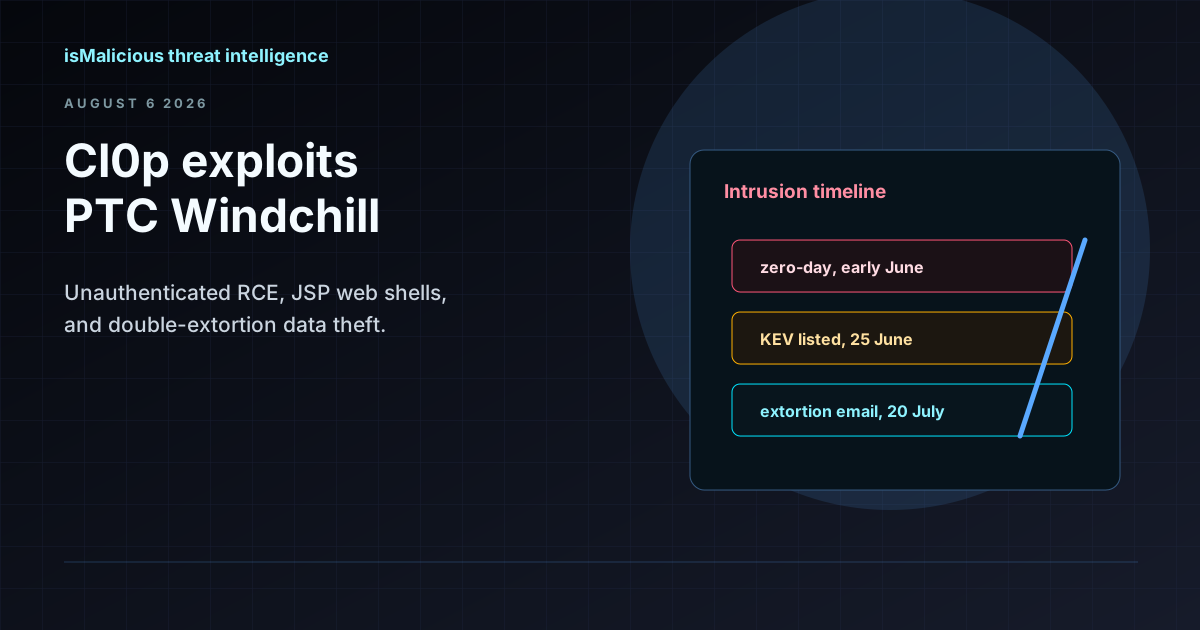
Cl0p Is Exploiting PTC Windchill (CVE-2026-12569) to Steal Engineering Data
A Cl0p affiliate is chaining a FlexPLM information disclosure with an unauthenticated RCE in PTC Windchill to plant JSP web shells and run double-extortion data theft. Here are the detection signals and the triage workflow.
Infostealer Log Marketplaces: How Stolen Corporate Credentials End Up for Sale
Stealer-log marketplaces are booming in 2026, trading stolen corporate cookies, passwords, and SaaS sessions that fuel ransomware access and bypass MFA.
Subdomain Enumeration for Security Teams: Attack Surface Discovery and DNS Reconnaissance
Subdomain enumeration surfaces forgotten dev servers, dangling DNS, and shadow IT before attackers do. Passive and active recon techniques compared.
isMalicious vs GreyNoise: IP Noise Scoring and Threat Intelligence API Compared
GreyNoise tags internet background noise; isMalicious adds verdicts, WHOIS, DNS history, and ransomware context. A SOC-focused comparison for triage teams.

Agentic AI Threat Mapping: MITRE ATT&CK Needs Evidence-Rich Workflows
Anthropic mapped AI-enabled cyber activity to MITRE ATT&CK and found gaps around autonomous orchestration. SOC teams need AI summaries tied to evidence, not unsupported verdicts.

AMOS macOS Infostealer: ClickFix Shows Why Hash Reputation Must Cover Developer Macs
AMOS and related macOS infostealers are turning social engineering into credential theft. File hash reputation, URL scanning, and domain intelligence help teams respond before stolen tokens spread.