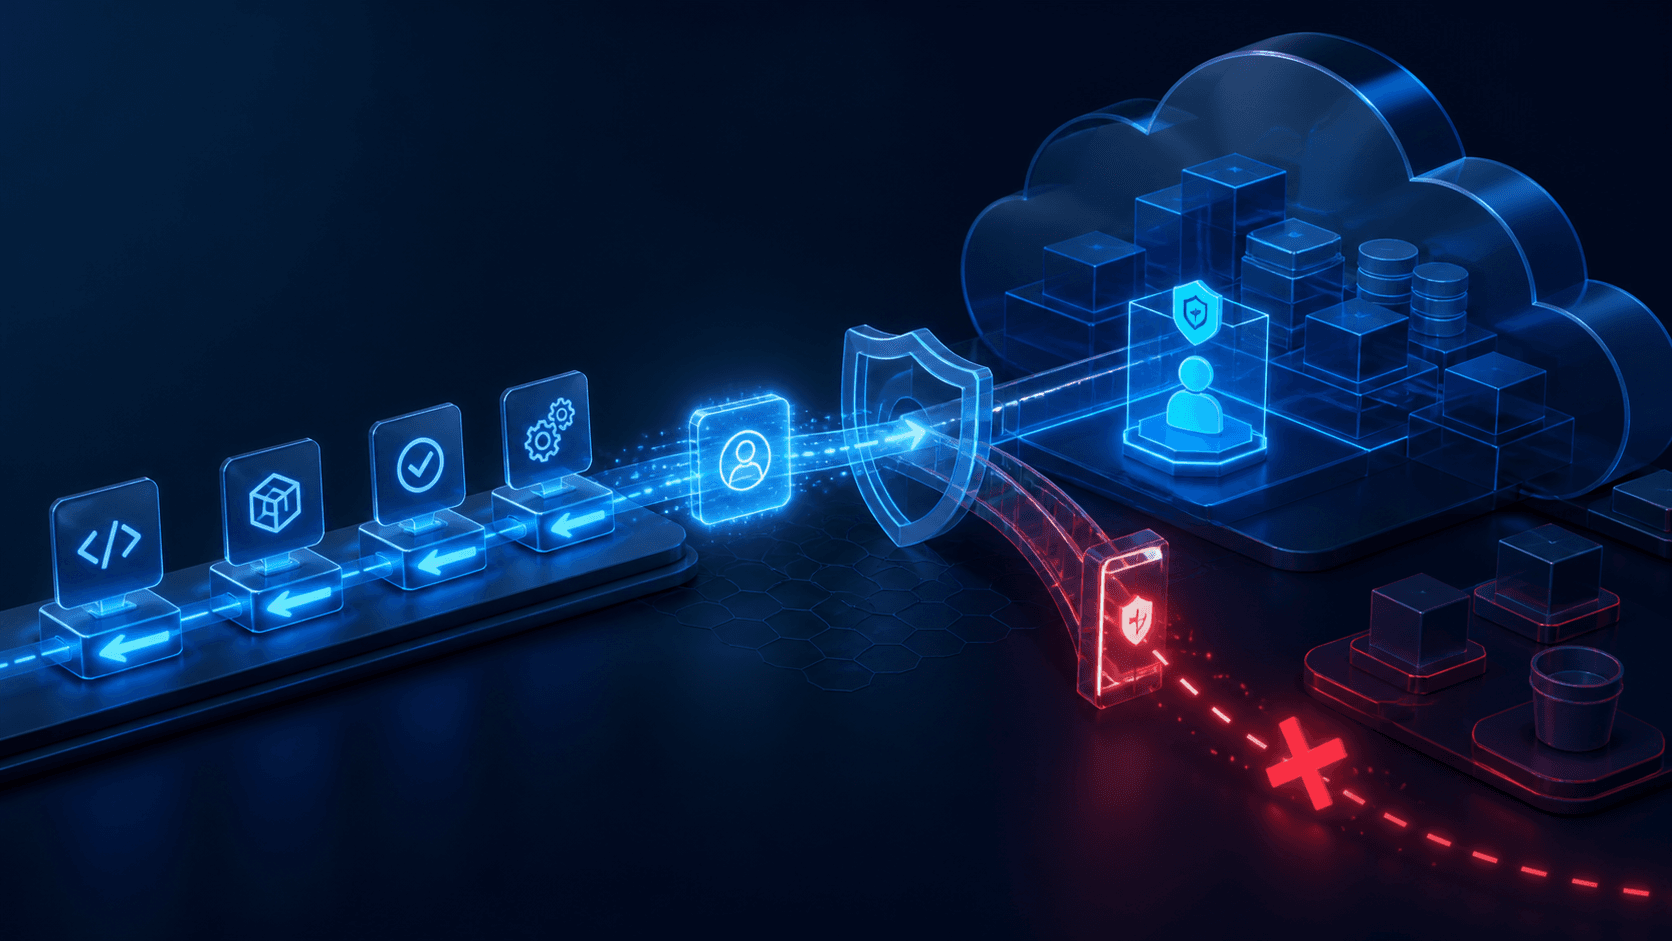
GitHub Actions OIDC: Secure Cloud Deployments
Replace long-lived cloud secrets with GitHub Actions OIDC while constraining claims, permissions, environments, reusable workflows, and incident response.
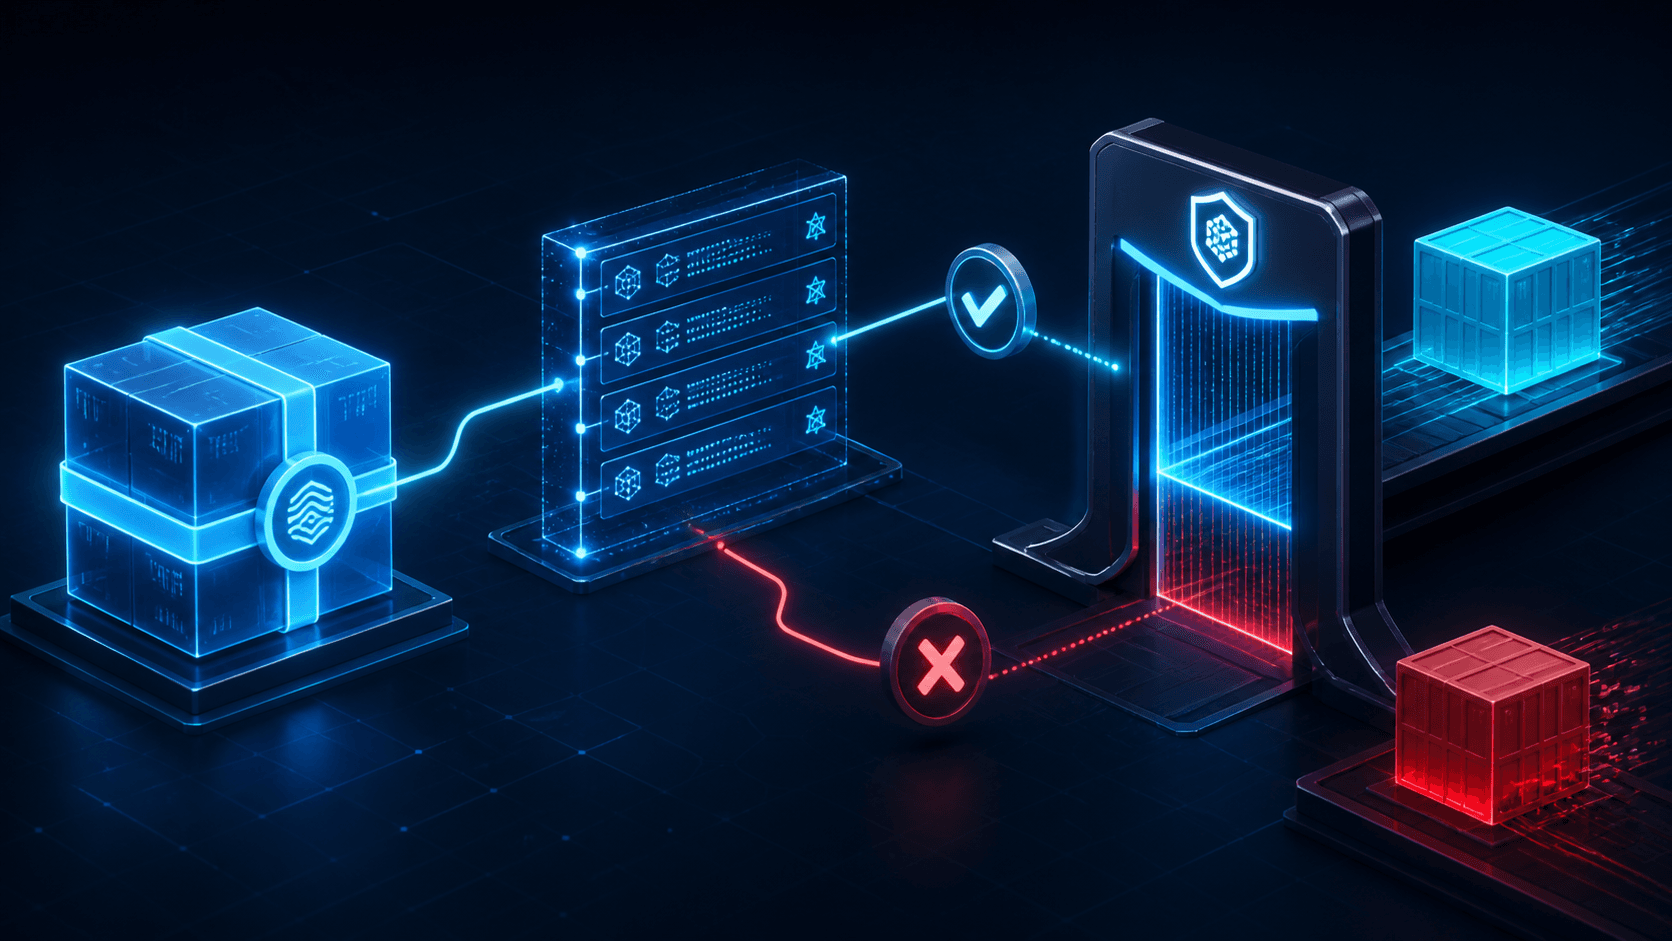
Sigstore and Cosign: Verify Container Images
Sign and verify container images with Cosign, keyless identities, transparency evidence, digest pinning, and admission policies that check the signer.
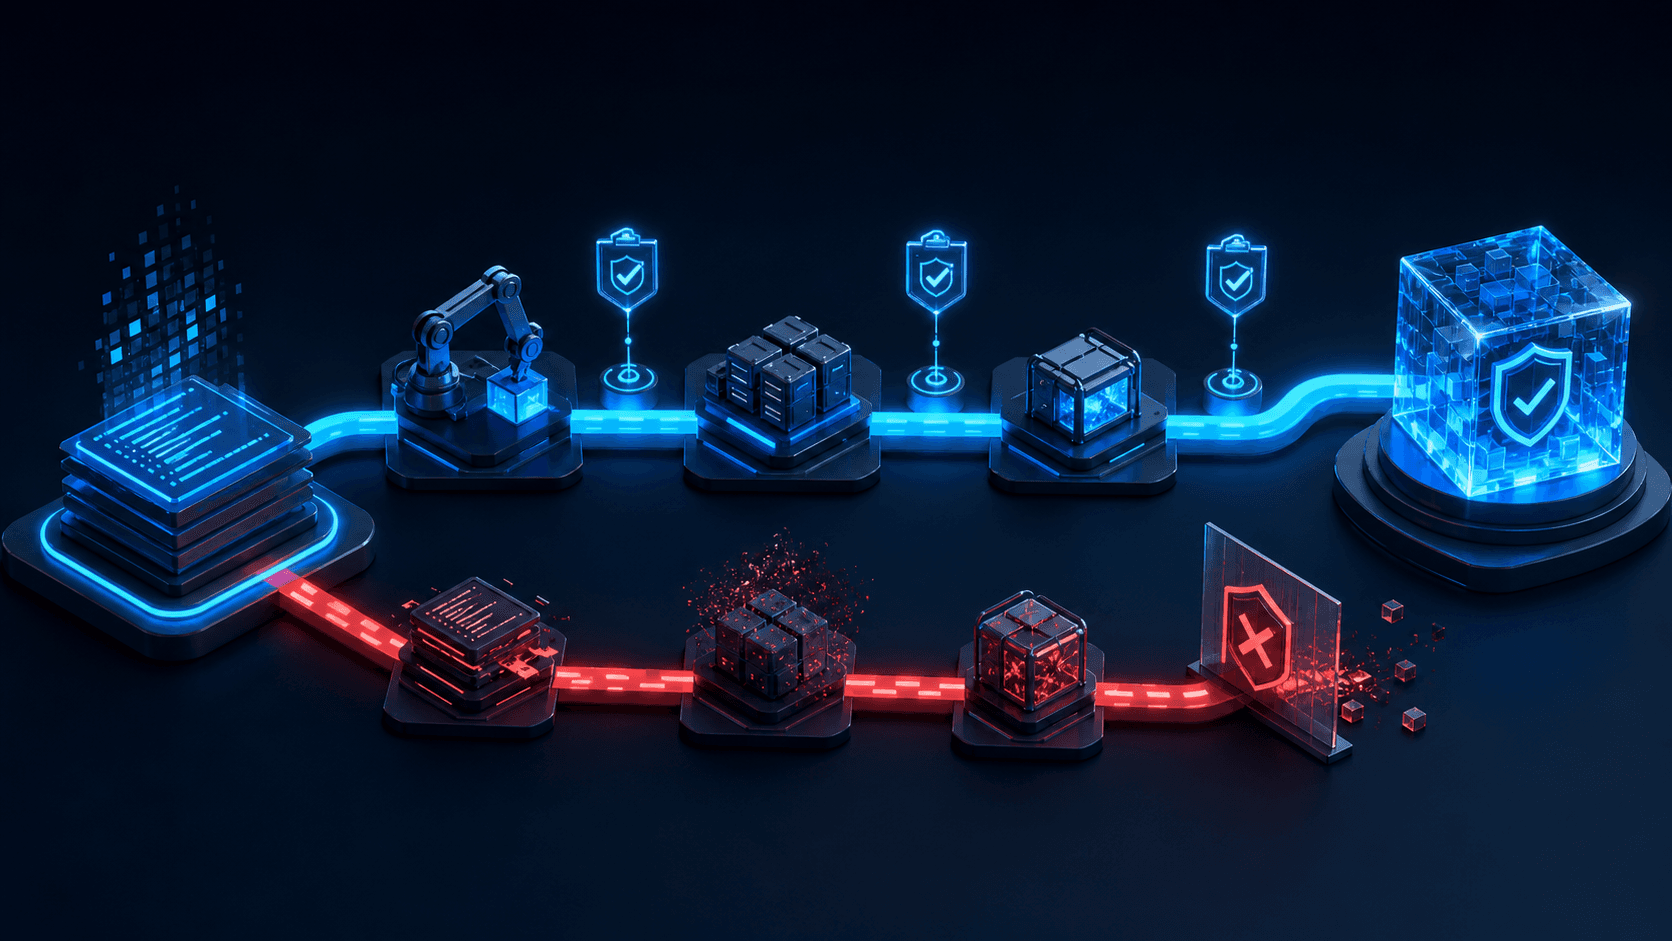
SLSA Provenance: Verify the Software Supply Chain
Use SLSA provenance to trace artifacts to source and build systems, verify expectations, improve CI controls, and respond to tampering.
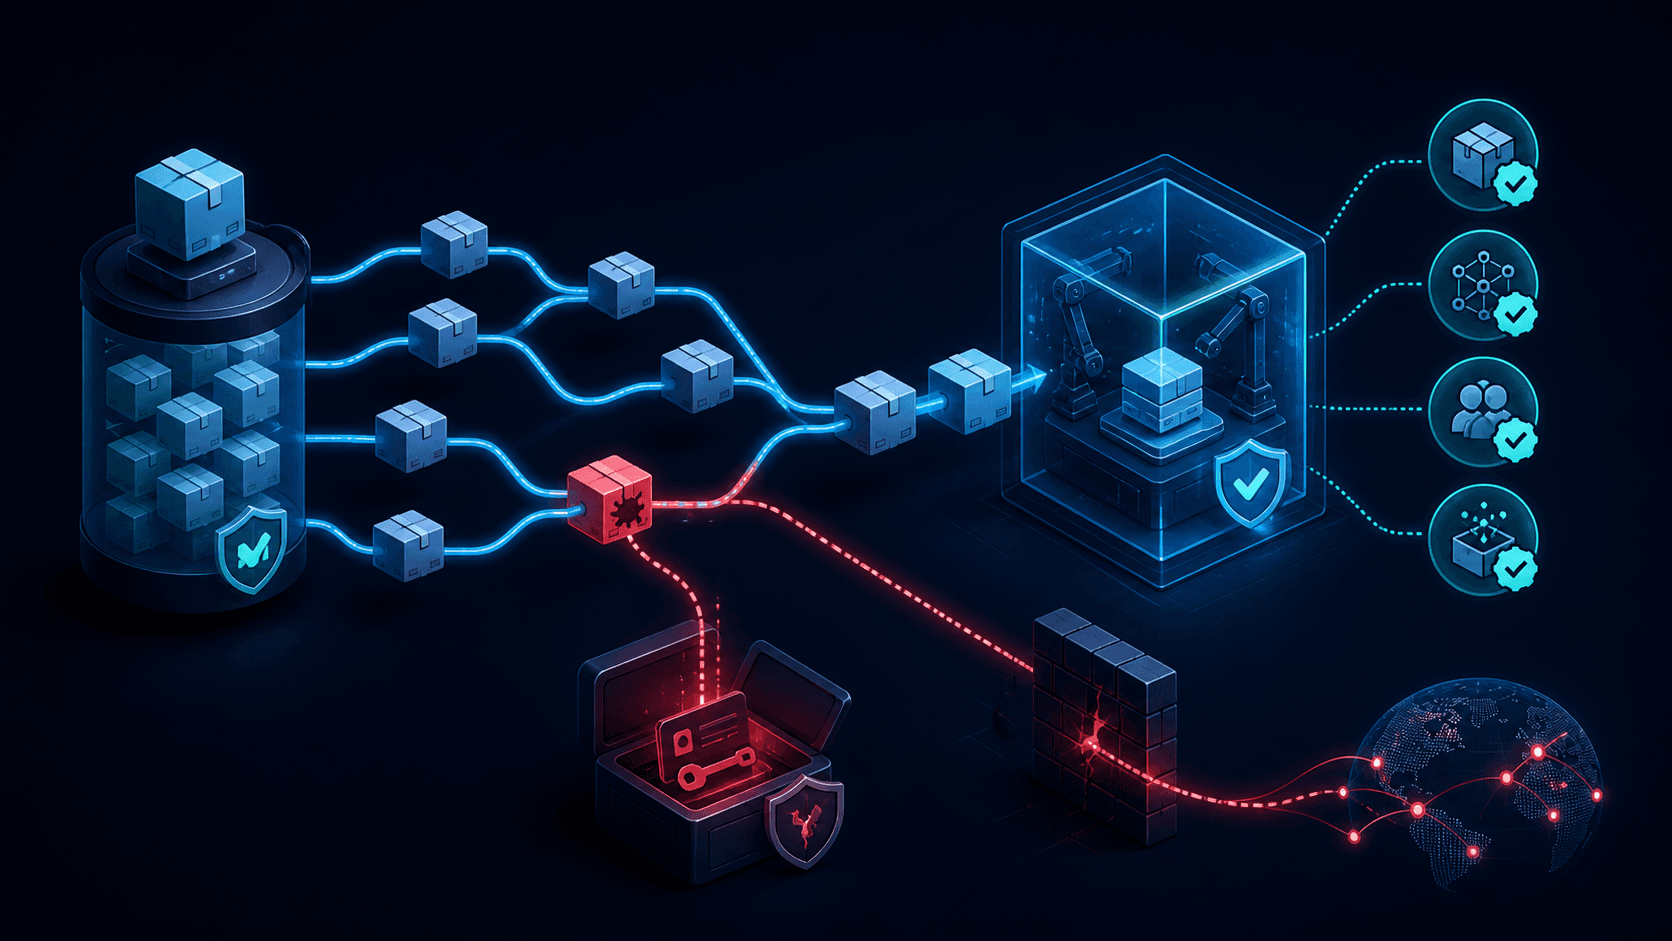
Malicious PyPI Packages: Detect Supply-Chain Attacks
Detect malicious PyPI packages through provenance, dependency controls, install behavior, network telemetry, hashes, and a Python incident playbook.
GitHub Actions and CI/CD Pipeline Compromise: A Growing Supply Chain Attack Vector
CI/CD pipeline compromises keep recurring across GitHub Actions ecosystems. Learn the detection signals, hardening steps, and enrichment workflow security teams need.

MCP Security Risks: Tool Poisoning, Prompt Injection, and the New AI Agent Attack Surface
Model Context Protocol integrations give agents access to tools, files, and services. That power creates new risks: tool poisoning, prompt injection, overbroad permissions, and untrusted server abuse.

Malicious npm Packages: Detecting Open-Source Supply Chain Compromise
Malicious npm packages use typosquatting, dependency confusion, install scripts, and maintainer compromise to steal secrets and backdoor builds. Learn practical detection and response.
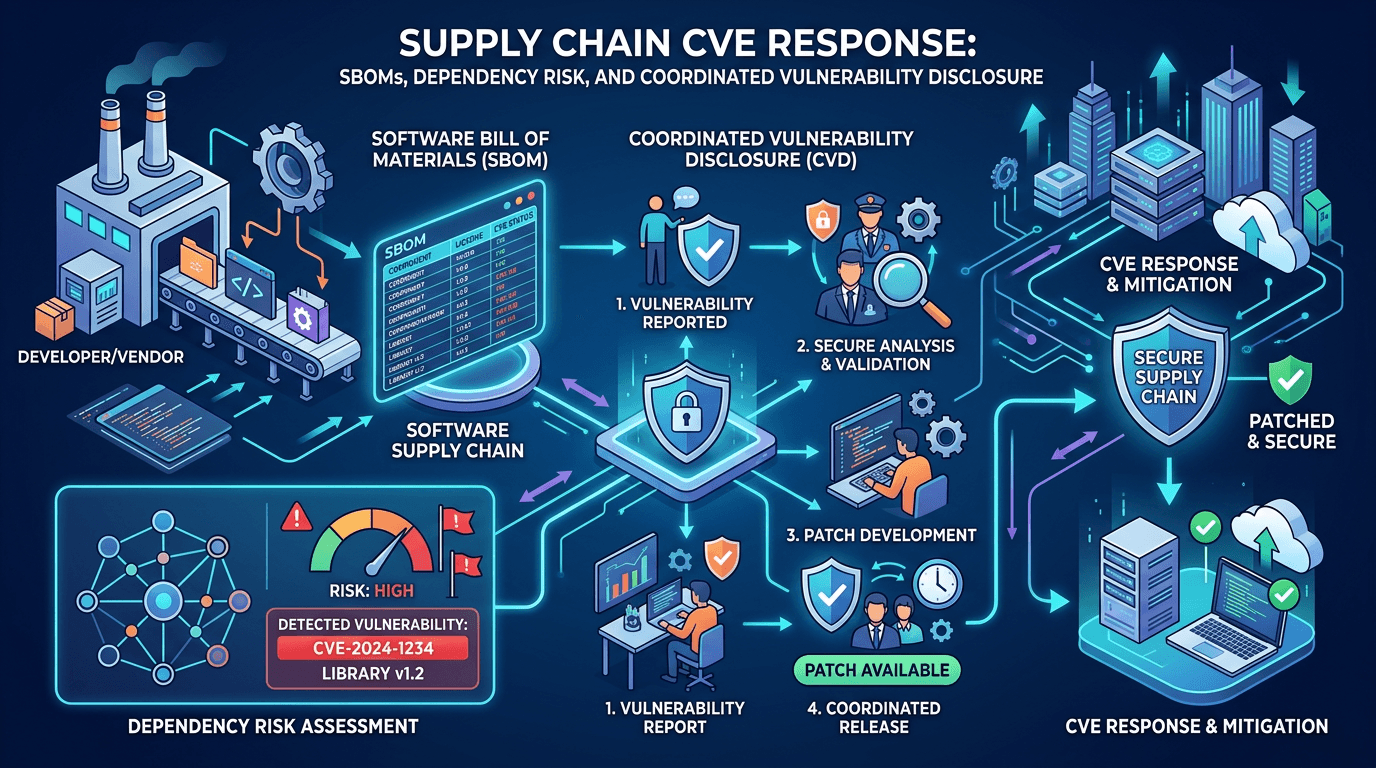
Supply Chain CVE Response: SBOMs, Dependency Risk, and Coordinated Vulnerability Disclosure
Build a modern supply-chain security program: generate SBOMs, map CVEs to components, integrate EPSS and KEV, and coordinate fixes across vendors and open-source maintainers.
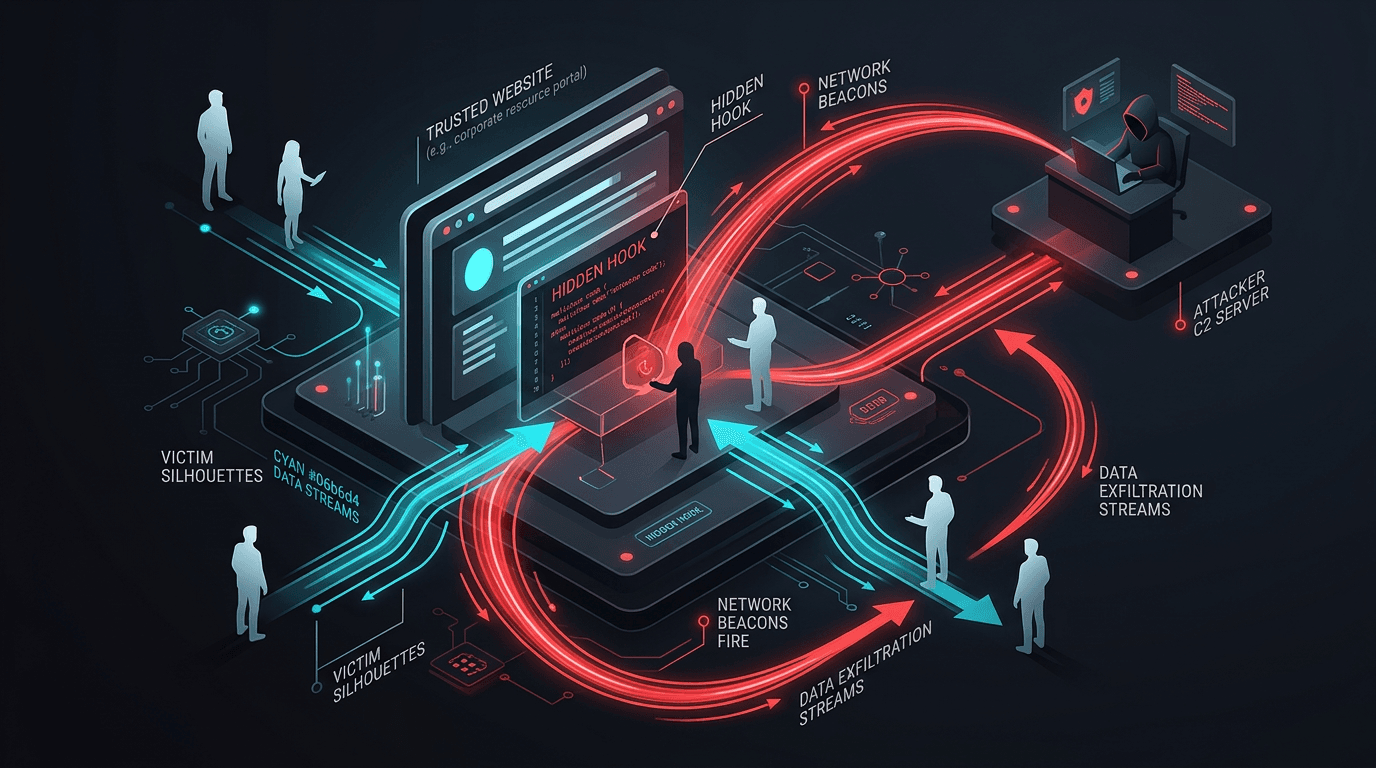
Watering Hole Attacks: Compromising the Sites Your Victims Already Trust
Instead of spear-phishing individuals, APTs infect websites their targets routinely visit. Learn how watering hole campaigns work and how to harden web supply chains and detection.