Threat Intelligence Blog
Research, insights, and updates from the isMalicious team. Page 2 of 10.

isMalicious API: Make Your First Reliable IOC Lookup
Call the current isMalicious IOC endpoint safely, handle failures, log useful evidence, and move from a terminal test to production.
TAXII Threat Feeds: Build a Continuous SIEM Integration
Connect an isMalicious TAXII collection to your SIEM with safe pagination, durable checkpoints, validation, monitoring, and recovery.

Blocklists for Operational Threat Prevention: Test and Roll Back
Use /app/blocklists to select, test, deploy, measure, and safely reverse IP or domain prevention controls.
Threat Report History: Recheck, Monitor, and Reuse Evidence
Use isMalicious report history to find earlier lookups, run fresh checks, add indicators to monitoring, create cases, and export a reusable lookup index.
Threat Intelligence Sources: Evaluate Evidence Before You Act
Use isMalicious Sources and Threat Patterns to examine freshness, contribution, agreement, coverage, and corpus-wide patterns before turning a detection into action.
CVE Watch Perimeters: Prioritize Findings by Real Exposure
Map products to CVE Watch perimeters, then combine active exploitation, CISA KEV, EPSS, CVSS, product context, and remediation status to focus vulnerability work.

isMalicious vs Spamhaus: DNSBL Blocklists and Threat Enrichment Serve Different Layers
Spamhaus DROP and SBL are the standard for mail and network DNSBL blocking. isMalicious adds REST enrichment, URL scoring, CVE context, and STIX feeds. Most mature stacks use both at different layers.
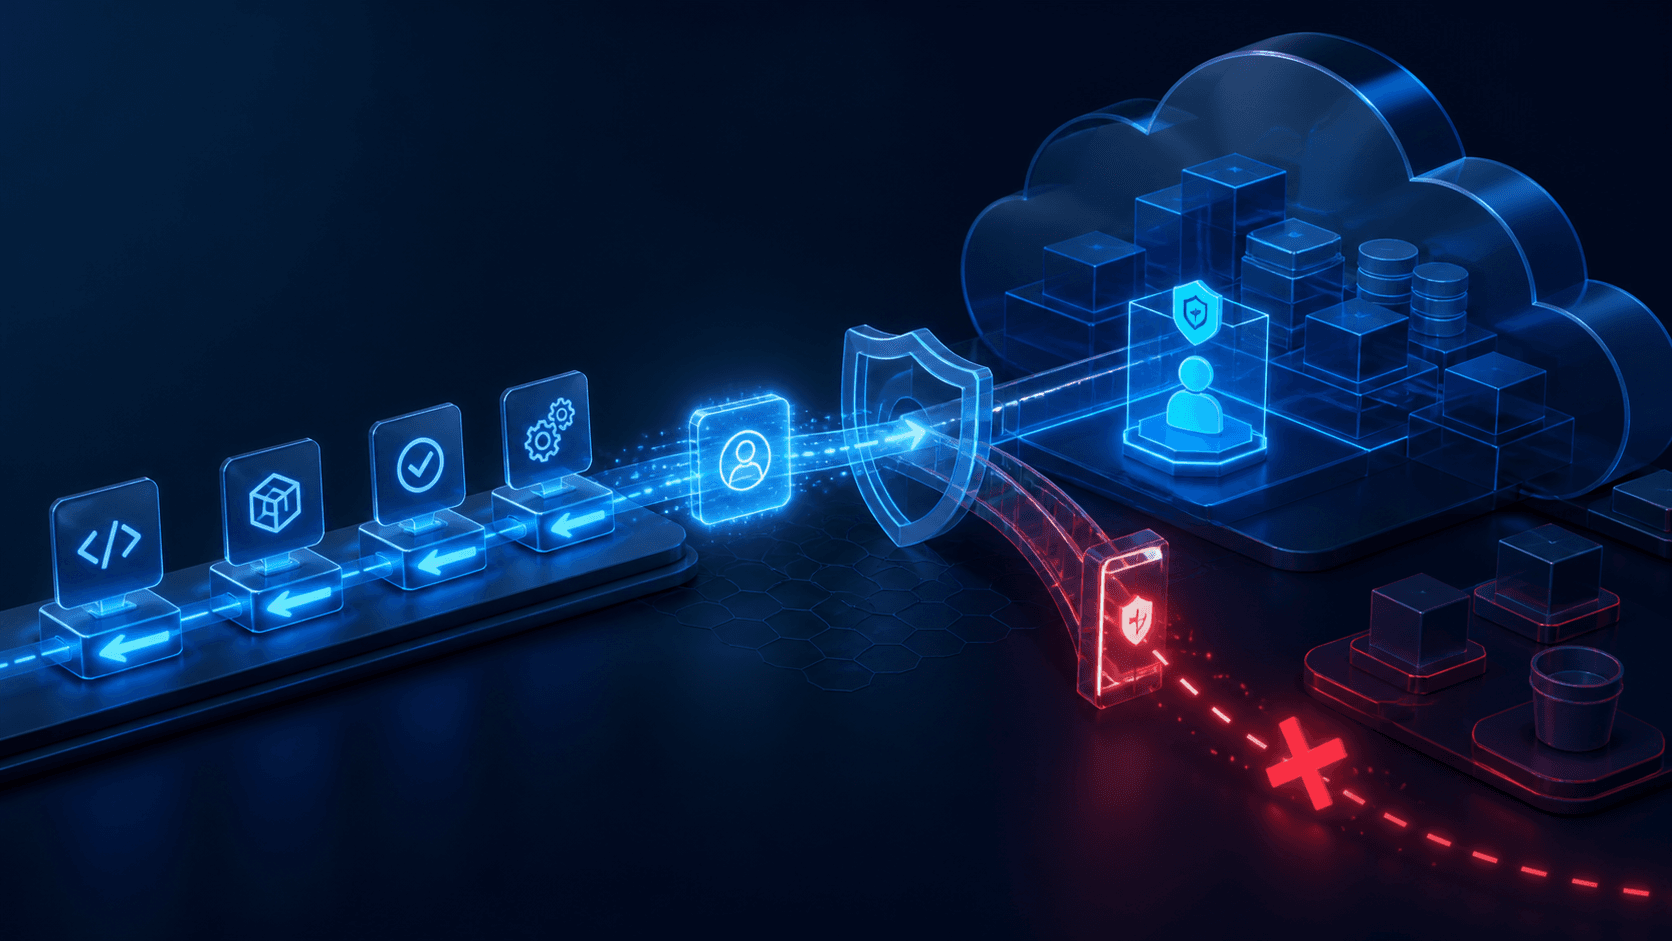
GitHub Actions OIDC: Secure Cloud Deployments
Replace long-lived cloud secrets with GitHub Actions OIDC while constraining claims, permissions, environments, reusable workflows, and incident response.
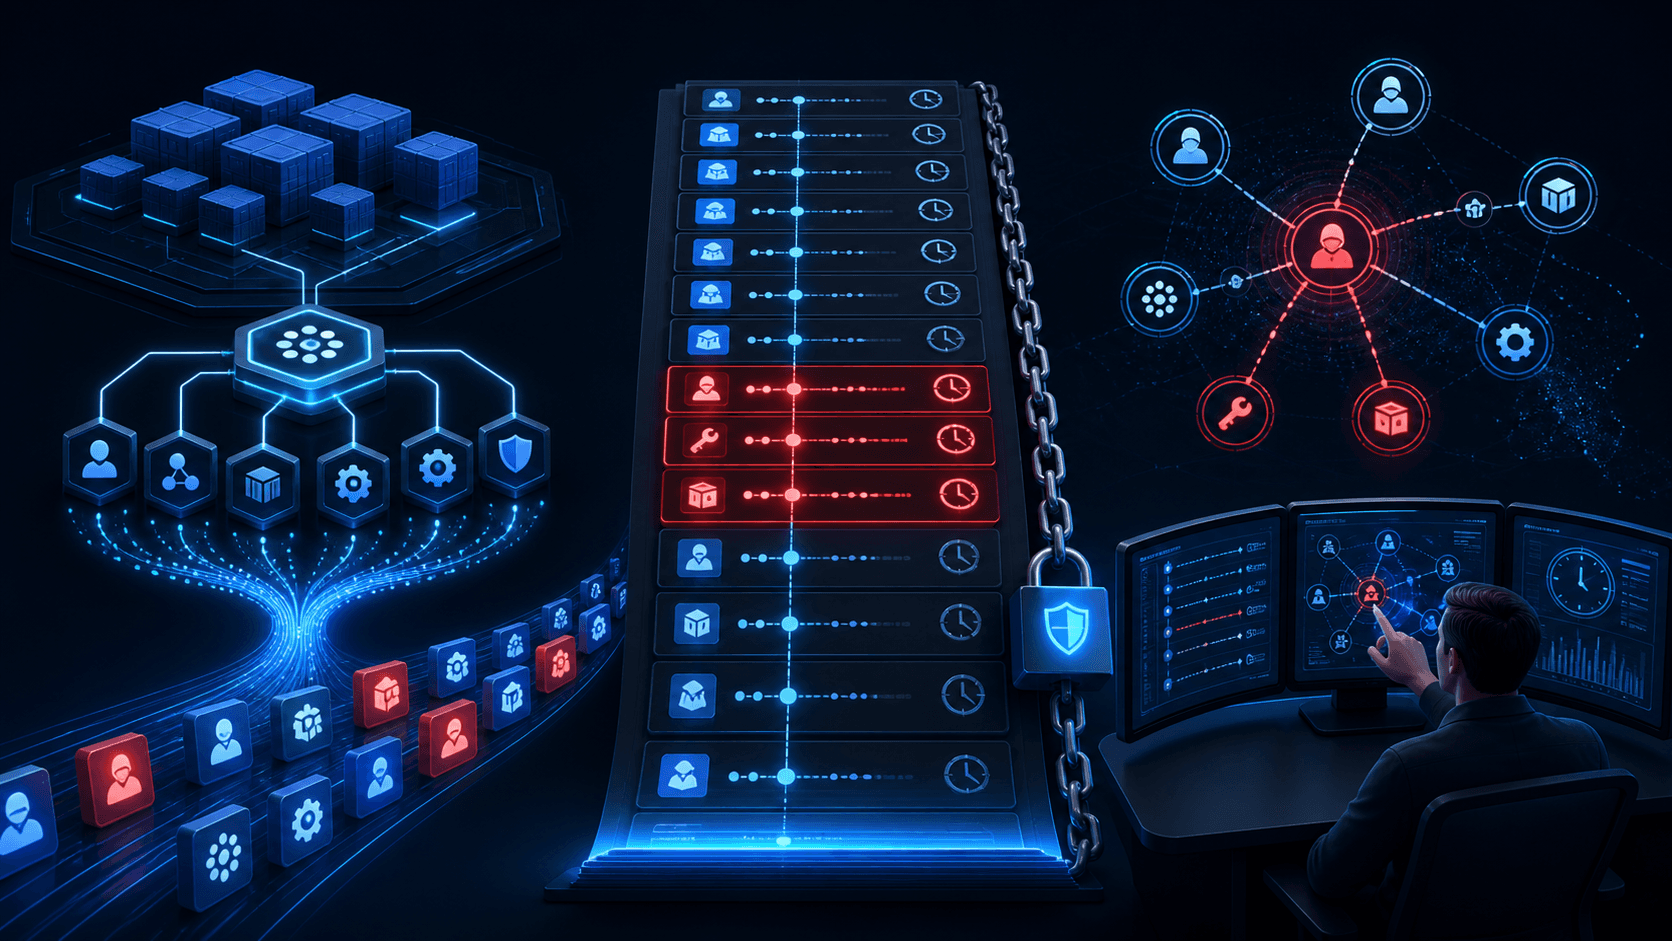
Kubernetes Audit Logs: Threat Detection Guide
Turn Kubernetes audit logs into detections for privilege abuse, secret access, persistence, risky exec, and control-plane compromise.
eBPF Runtime Security for Kubernetes
Use eBPF runtime security to observe processes, files, privileges, and network activity in Kubernetes while controlling noise and enforcement risk.
Sigstore and Cosign: Verify Container Images
Sign and verify container images with Cosign, keyless identities, transparency evidence, digest pinning, and admission policies that check the signer.
SLSA Provenance: Verify the Software Supply Chain
Use SLSA provenance to trace artifacts to source and build systems, verify expectations, improve CI controls, and respond to tampering.
Malicious PyPI Packages: Detect Supply-Chain Attacks
Detect malicious PyPI packages through provenance, dependency controls, install behavior, network telemetry, hashes, and a Python incident playbook.
YARA vs Sigma: Which Detection Rule Should You Use?
Compare YARA and Sigma by data source, purpose, portability, performance, false positives, testing, and threat-intelligence workflow.
MFA Fatigue: Stop Push-Bombing Attacks
Detect and prevent MFA fatigue with number matching, rate limits, risk signals, phishing-resistant authentication, and an identity incident playbook.
HTML Smuggling: Detection and Incident Response
Detect HTML smuggling by correlating browser file creation, JavaScript Blob behavior, download telemetry, endpoint execution, and threat intelligence.
Browser-in-the-Browser Phishing: Detection Guide
Understand browser-in-the-browser phishing, spot fake SSO windows, detect campaign infrastructure, and reduce risk with phishing-resistant authentication.

Subdomain Takeover: Find Dangling DNS First
Prevent subdomain takeover by finding dangling DNS records, linking names to cloud owners, monitoring certificates, and fixing decommissioning order.
Bulletproof Hosting: Map Criminal Infrastructure
Identify bulletproof hosting through ASN, prefix, domain, abuse, migration, and campaign signals without treating an entire network as malicious.

Domain Shadowing: Detect Compromised DNS at Scale
Detect domain shadowing by monitoring DNS changes, certificate issuance, subdomain behavior, account security, and infrastructure relationships.

JA4 TLS Fingerprinting for Threat Hunting
Use JA4 TLS fingerprints for threat hunting, malware clustering, allowlisting, and anomaly detection without treating a fingerprint as identity.

DNS over HTTPS Security: Detect DoH Abuse
Secure DNS over HTTPS without losing visibility: govern resolvers, detect bypass attempts, correlate endpoint telemetry, and preserve user privacy.

Certificate Transparency for Phishing Detection
Use Certificate Transparency logs to find rogue certificates, phishing subdomains, brand impersonation, and exposed assets before they become incidents.
IPv6 Threat Intelligence: Reputation Beyond IPv4
Build IPv6 threat intelligence with correct normalization, prefix context, dual-stack logging, enrichment, and reputation decisions that avoid overblocking.
Subscribe to Our Newsletter
Weekly threat intelligence insights delivered to your inbox.