How to Analyze Suspicious Email Headers
Identify trusted servers, interpret Authentication-Results, and investigate a suspicious email without confusing authentication with safe content.
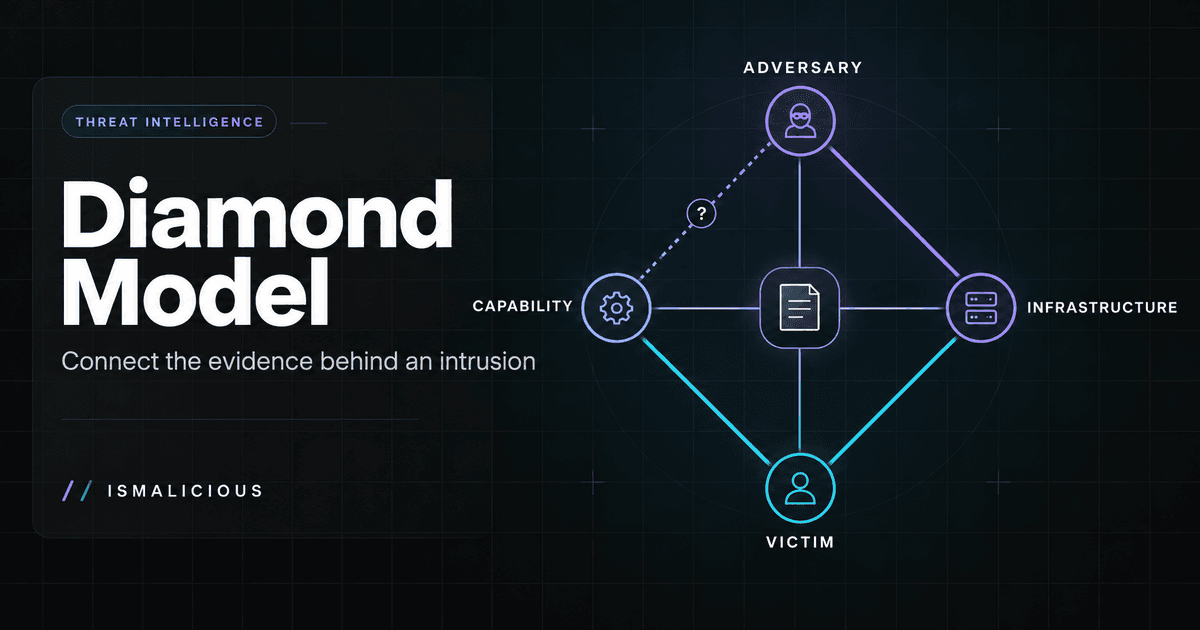
Diamond Model: A Practical CTI Investigation Walkthrough
Use the Diamond Model to connect evidence, test competing explanations, build activity threads, and turn a phishing investigation into defensible decisions.
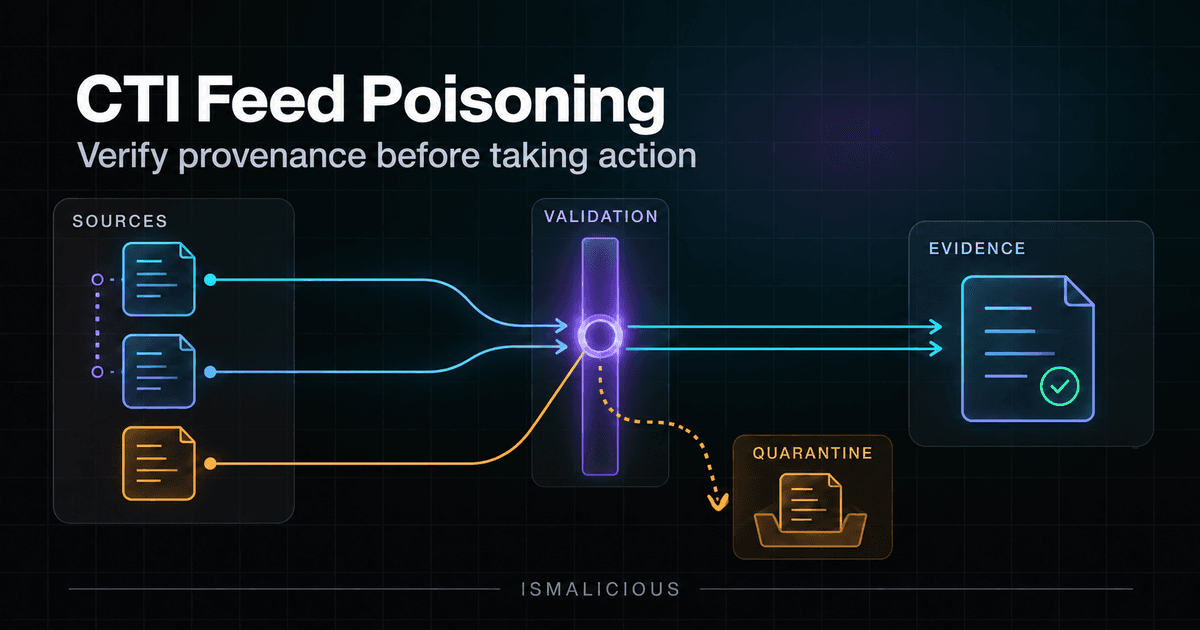
Threat Intelligence Feed Poisoning: Protect Your Evidence
Protect CTI decisions from misleading data with source provenance, mirror detection, contradiction handling, safe ingestion, human review, and tested rollback.
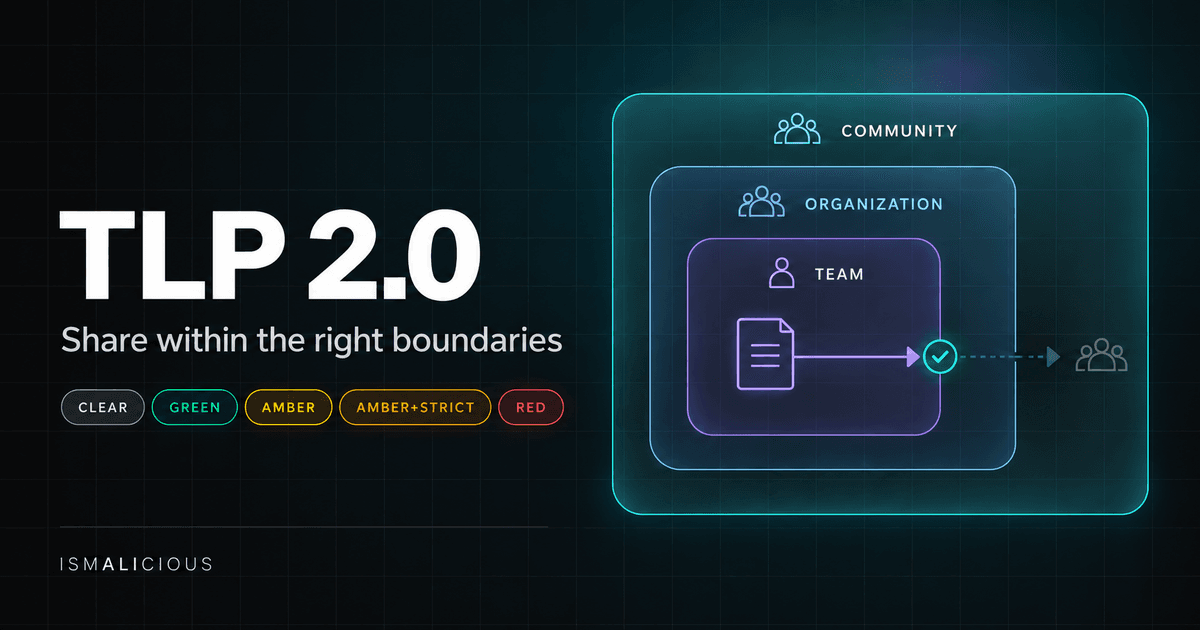
TLP 2.0: Share Threat Intelligence Without Leaking Data
Apply TLP 2.0 to CTI reports, indicators, and supplier exchanges with practical sharing boundaries, permission checks, data minimization, and export controls.

Investigate an IOC Alert: Link IP, DNS and Process Logs
An IOC match is an investigation lead. Correlate DNS, network connections and process records to establish what happened on the endpoint.

IP Blacklisted? Check for a False Positive Before Blocking
Check DNSBL scope, shared IPs, stale evidence and lookup errors to find why an IP was blacklisted and choose a proportionate response.
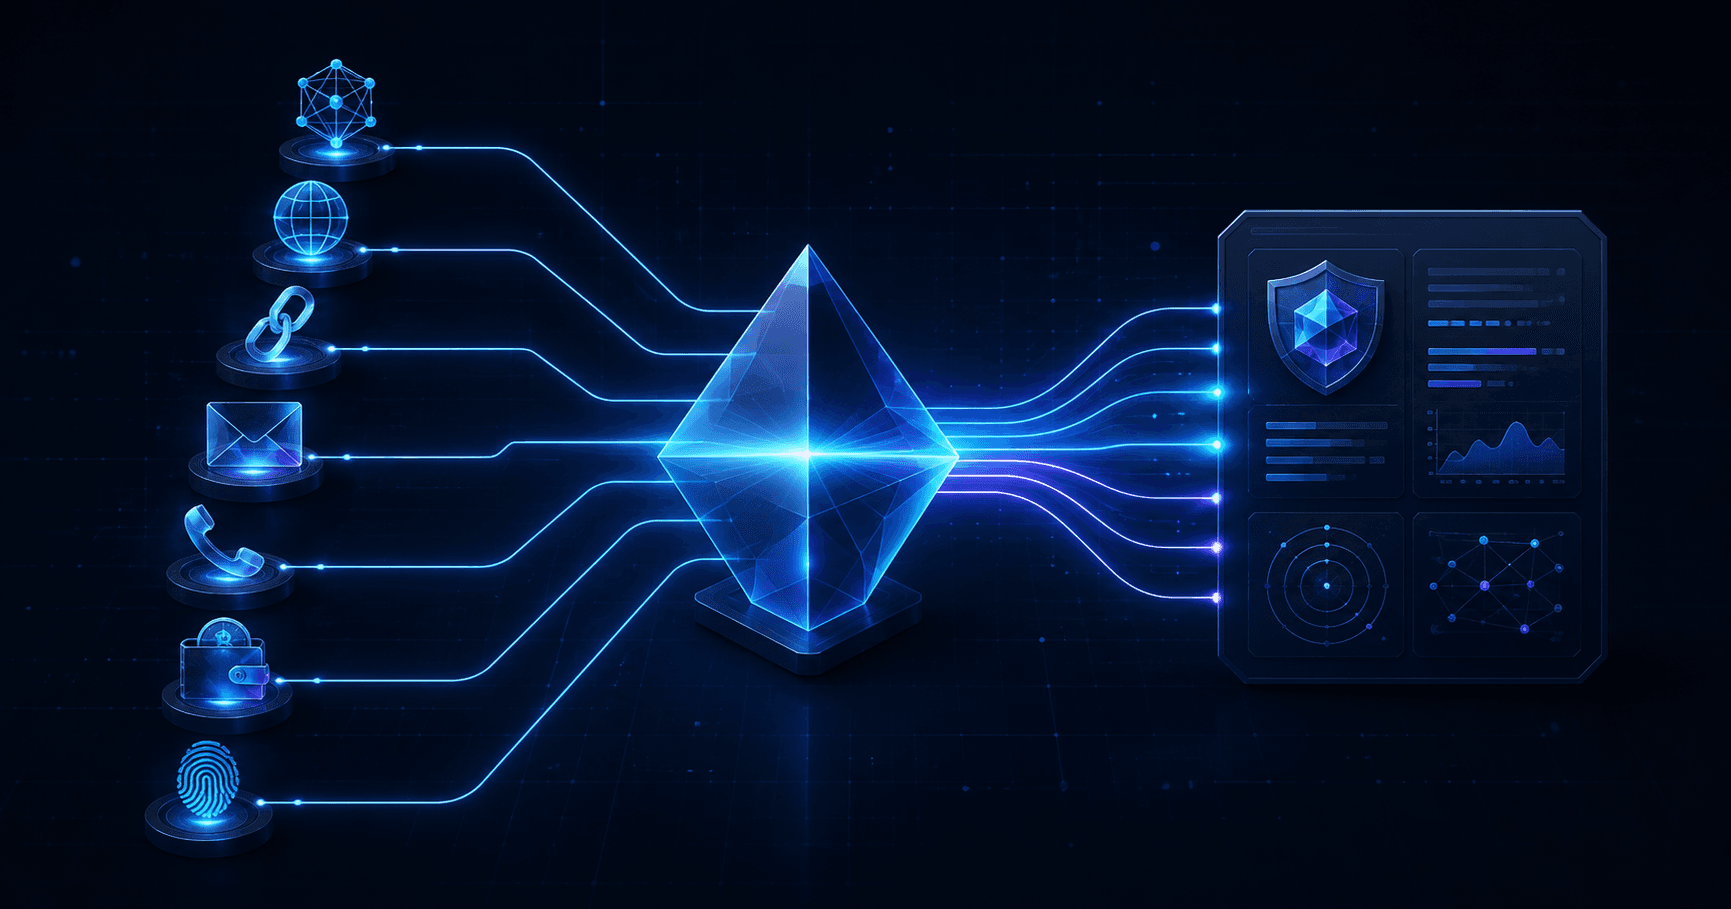
Smart Lookup: Check Any Threat Indicator from One Search
Paste an IP, domain, URL, email, phone number, wallet, file hash, or a complete suspicious message. Smart Lookup routes each indicator to the right threat report.
Composite Threat Reports: Triage Multiple IOCs Together
A phishing message or security alert rarely contains one indicator. Use a composite threat report to scope several IOCs without losing the evidence behind each result.
Threats Dashboard: Turn Current Intelligence into Priorities
Use the isMalicious Threats dashboard to move from a broad threat picture to the sectors, ransomware groups, malware, victims, and evidence that matter to your team.
Threat Alerts and Action Center: Build a Response Workflow
Move from monitored indicators and incoming alerts to a ranked queue, analyst validation, and owned response work with isMalicious Alerts and Action Center.
isMalicious API: Make Your First Reliable IOC Lookup
Call the current isMalicious IOC endpoint safely, handle failures, log useful evidence, and move from a terminal test to production.
Threat Report History: Recheck, Monitor, and Reuse Evidence
Use isMalicious report history to find earlier lookups, run fresh checks, add indicators to monitoring, create cases, and export a reusable lookup index.
Threat Intelligence Sources: Evaluate Evidence Before You Act
Use isMalicious Sources and Threat Patterns to examine freshness, contribution, agreement, coverage, and corpus-wide patterns before turning a detection into action.

isMalicious vs Spamhaus: DNSBL Blocklists and Threat Enrichment Serve Different Layers
Spamhaus DROP and SBL are the standard for mail and network DNSBL blocking. isMalicious adds REST enrichment, URL scoring, CVE context, and STIX feeds. Most mature stacks use both at different layers.
IPv6 Threat Intelligence: Reputation Beyond IPv4
Build IPv6 threat intelligence with correct normalization, prefix context, dual-stack logging, enrichment, and reputation decisions that avoid overblocking.

Fast-Flux DNS: Detect Rotating Attack Infrastructure
Learn how to detect fast-flux DNS using TTL, passive DNS, ASN diversity, reputation signals, and a repeatable SOC investigation workflow.
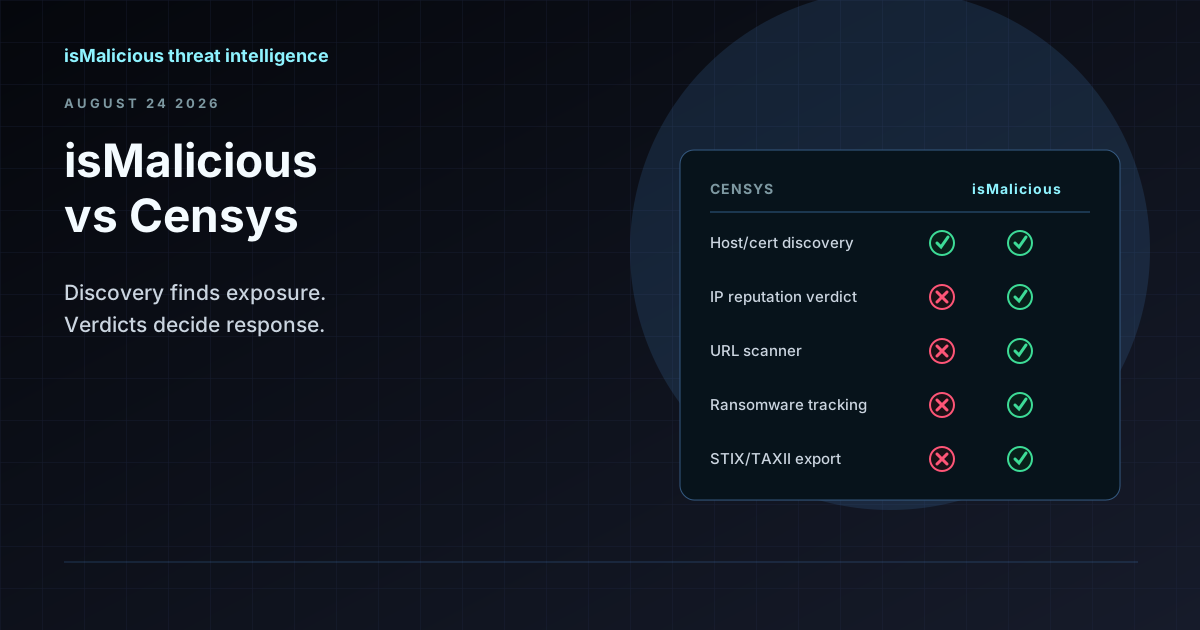
isMalicious vs Censys: Internet Discovery and Reputation Verdicts Are Different Jobs
Censys maps what exists on the internet — hosts, certificates, open ports. isMalicious assesses what is malicious. Most teams comparing the two need the second question answered, not the first.
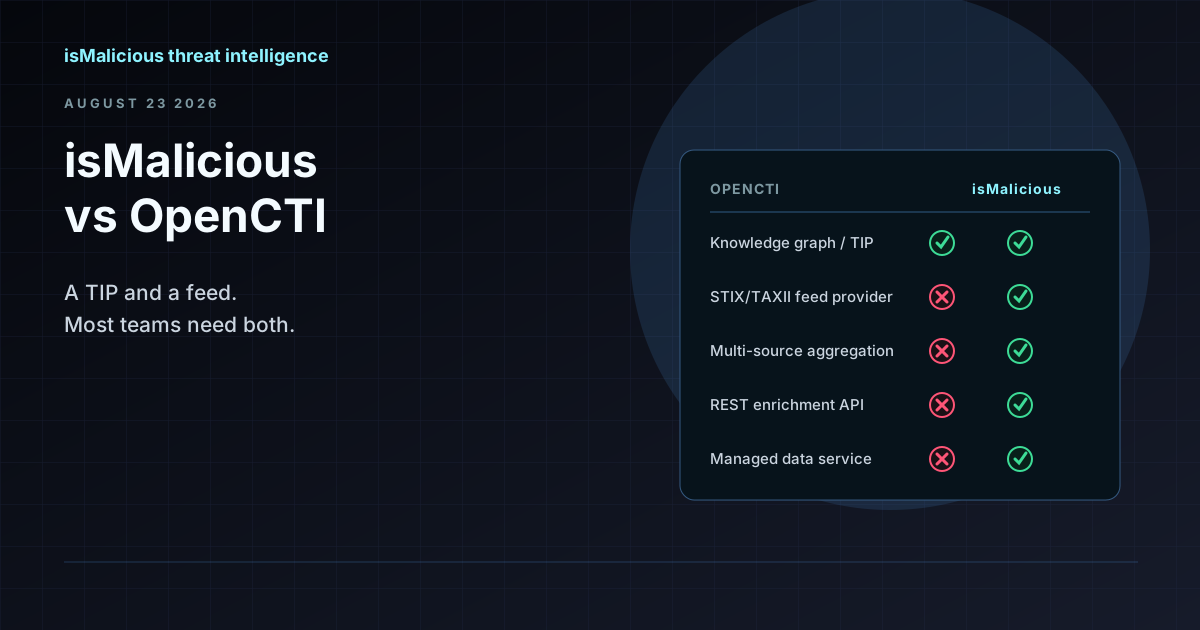
isMalicious vs OpenCTI: Why This Is the Wrong Comparison (and How They Work Together)
OpenCTI is a threat intelligence platform and knowledge graph. isMalicious is a data provider that feeds it. Teams searching for an OpenCTI alternative usually need a feed, not a replacement TIP.
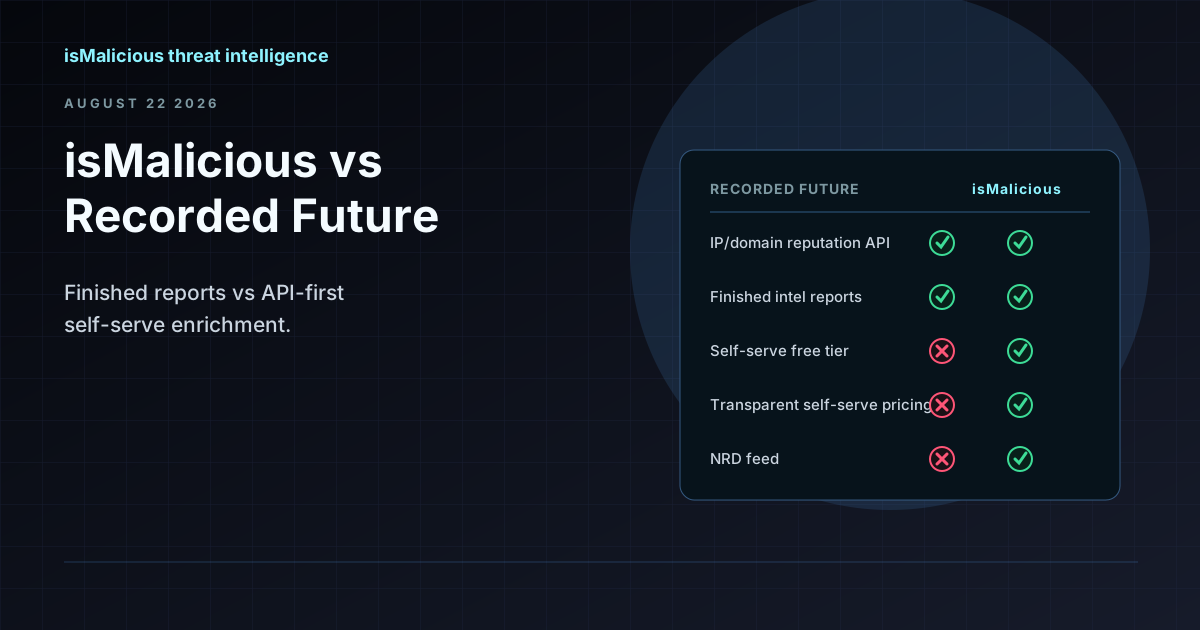
isMalicious vs Recorded Future: When a Threat Data API Makes More Sense Than an Enterprise Intel Program
Recorded Future delivers finished intelligence and analyst support at enterprise scale. isMalicious delivers self-serve enrichment and feeds without a sales cycle. The right choice depends on whether you need strategic reports or automated verdicts.

Firewall Blocklist Automation: Pulling IP and Domain Feeds Without Outages
External dynamic lists can block malware and phishing at the edge — or break payroll, CDN traffic, and vendor portals. This guide covers staged rollout, allowlists, fail-open vs fail-closed, and measuring hit rates for IP and domain blocklists.
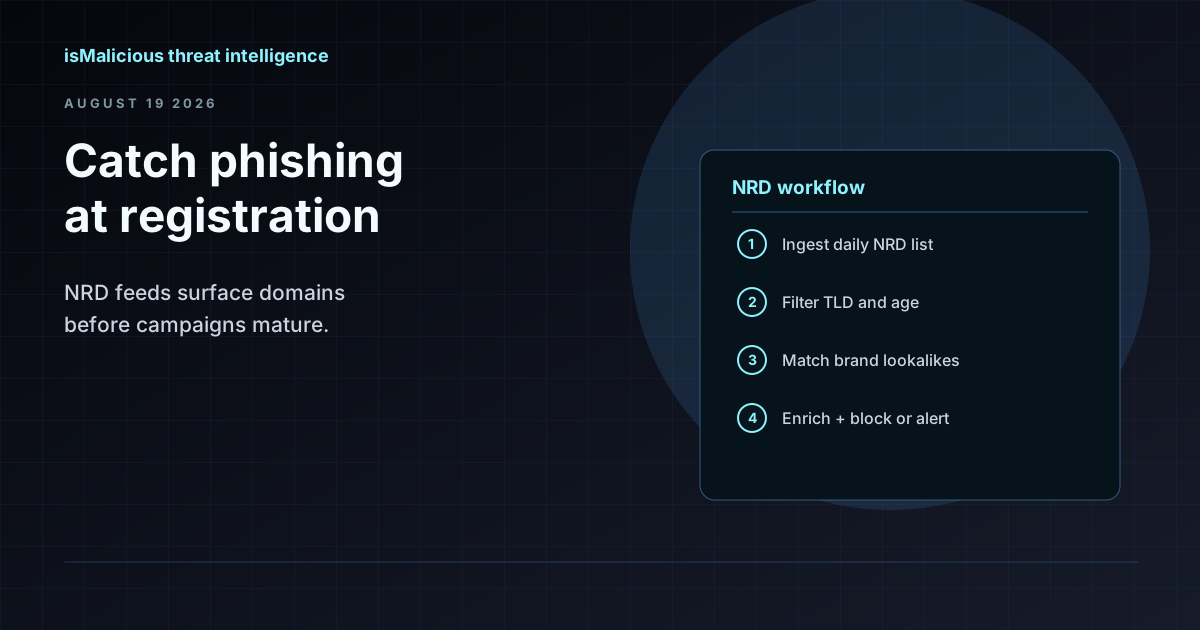
How to Use an NRD Feed to Catch Phishing Before It Lands in the Inbox
Newly registered domains are where most phishing campaigns start. This guide walks through NRD feed workflows for brand monitoring, mail gateway hygiene, and SOC triage — without treating domain age as a blunt block rule.
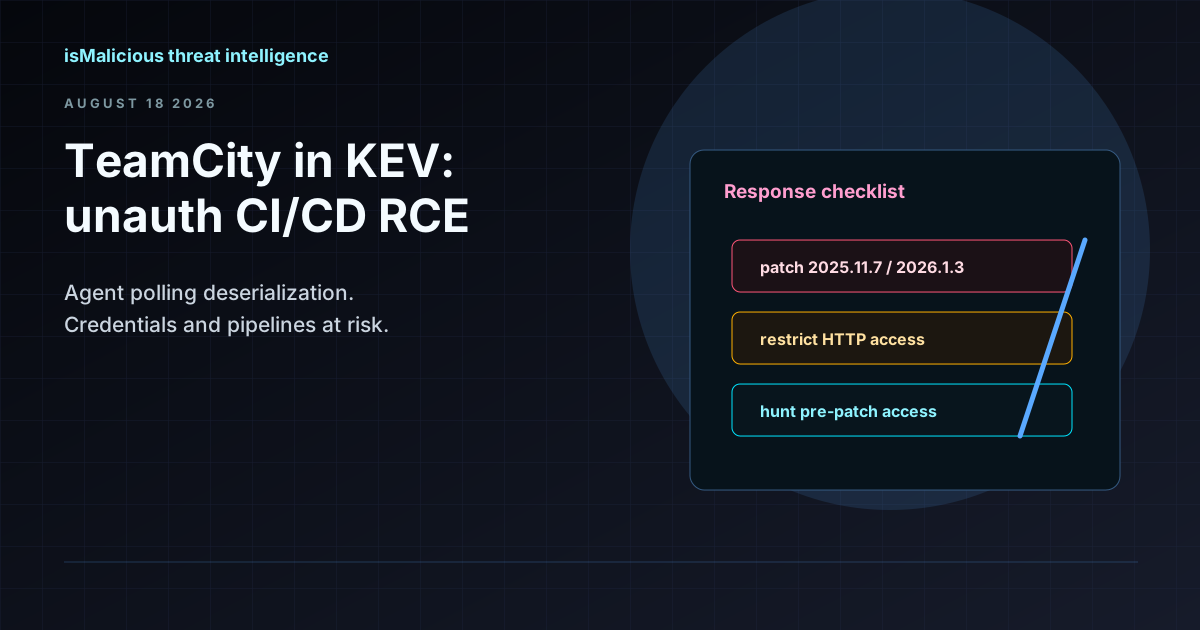
CVE-2026-63077 Puts Unauthenticated RCE on Every TeamCity On-Premises Server
A deserialization flaw in the agent polling protocol gives attackers TeamCity server privileges without credentials. JetBrains patched in 2025.11.7 and 2026.1.3 — CISA KEV and a 3-day federal deadline mean hunt now, not after the next release train.
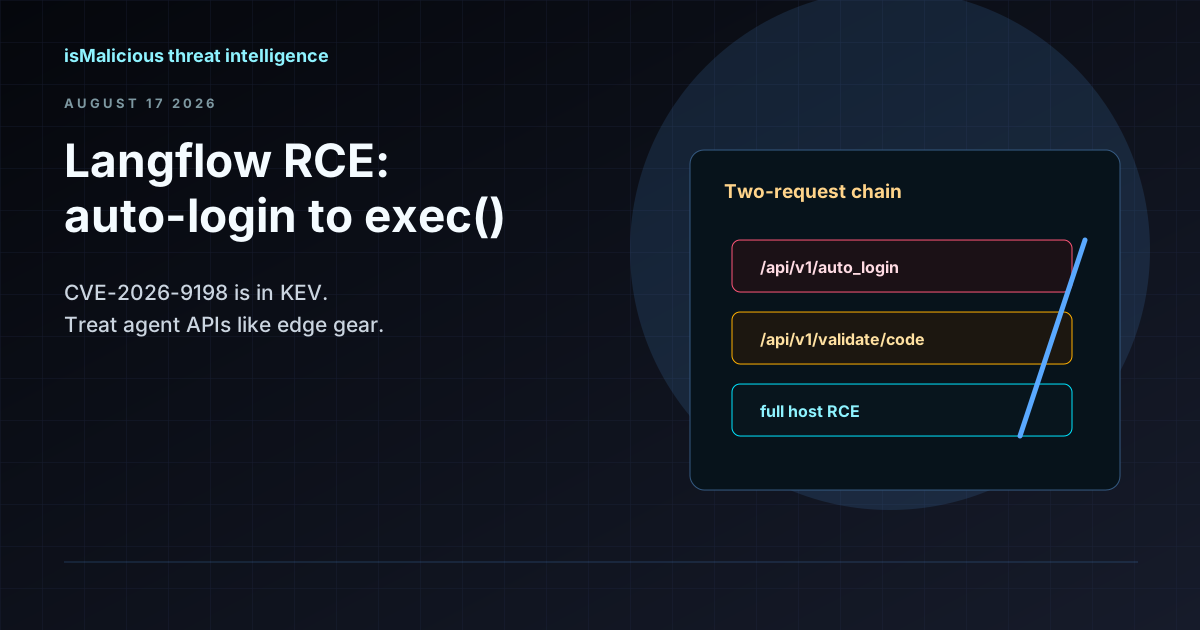
CVE-2026-9198 Gives Unauthenticated RCE in IBM Langflow OSS Agent Control Planes
A SUPERUSER token minted through /api/v1/auto_login chains with Python exec() in /api/v1/validate/code. Langflow 1.10.1 fixes the flaw — but internet-exposed instances need hunting now, not after the next sprint.
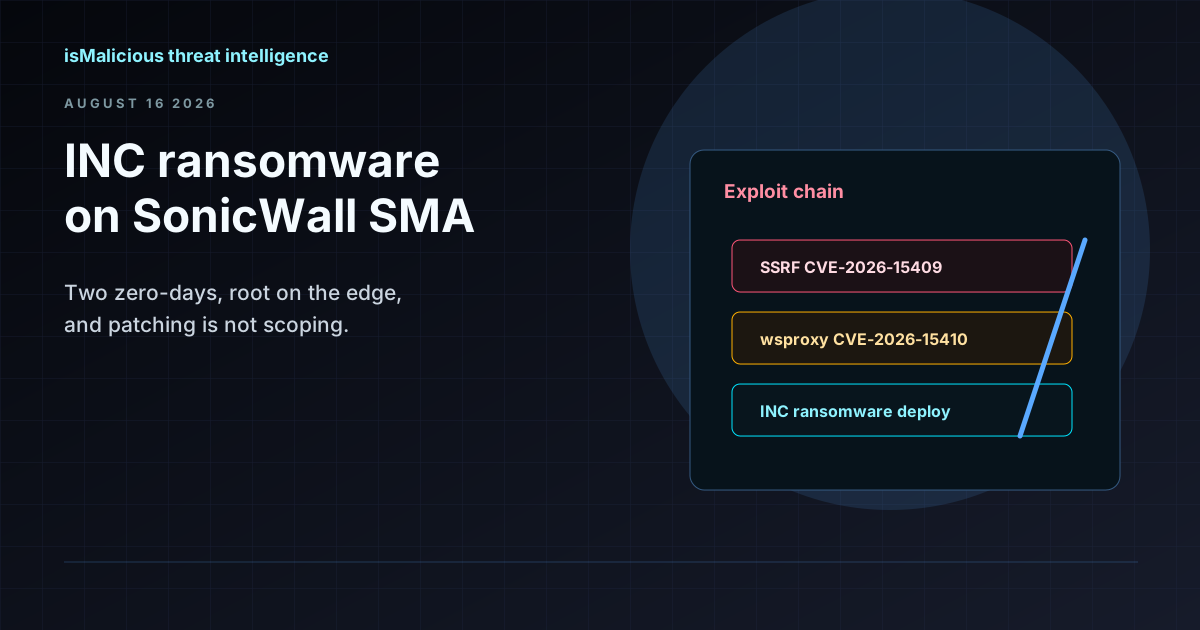
INC Ransomware Chains Two SonicWall SMA Zero-Days (CVE-2026-15409, CVE-2026-15410)
INC affiliates are weaponizing an SSRF and a post-authentication code injection in SonicWall SMA 1000 to reach internal networks. Exploitation started weeks before the July 14 patch — here is how to hunt and triage.